My taxi is slicing throughout city, and I’ve an necessary assembly in quarter-hour. However I am not frantically skimming notes. I am leaning again with my eyes closed, being briefed on my firm’s KPIs, buyer suggestions and media protection by a podcast narrated in a voice I created totally utilizing AI.
I constructed it the evening earlier than utilizing an AI agent. Later that evening, I fell asleep listening to the identical artificial communiqué, which, for a CEO operating an AI firm in 2026, feels someplace between evening’s relaxation and a fever dream.
This is what most articles about AI brokers will not admit: I am not significantly orderly. I inform the agent to do one factor. If it begins annoying me, I inform it to cease. That is the system.
Once I learn that 78% of executives lack sturdy confidence they may go an unbiased AI governance audit inside 90 days, a quantity from Grant Thornton’s 2026 AI Impression Survey, my response wasn’t stunning. After all, they could not go, and neither might I. The everyday repair is a governance framework, which is okay for a big group. However with a lean org chart, no person’s constructing a framework. You are transport. So listed here are the principles I really observe.
The explanation “inform it to cease when it annoys me” works more often than not is not that I am significantly cautious or organized. It is that the majority of what I hand an agent is reversible and inside. If one thing goes awry, the implications are a wasted afternoon reasonably than catastrophic. My governance is within the measurement of the error I am keen to danger.
For instance, we join an AI agent to our buyer assist instrument, Intercom. As soon as a day, it reads incoming inquiries and sends me a report grouped by difficulty, so I can monitor whether or not an issue is spiking. It touches actual buyer information, which technically makes it infrastructure. However it solely reads, and the output comes solely to me. Worst case, it writes a foul abstract, and I discover. Nothing’s on hearth.
However the “studying is innocent” logic has a restrict. If you give an agent learn entry to your inbox, anybody who emails you possibly can plant directions inside that e-mail that the agent reads and acts on. That is immediate injection, and you find yourself partly trusting the mannequin, however to not the purpose of falling for it. My workaround was giving the agent its personal e-mail handle and forwarding solely the related mail to it.
Earlier than I let something run unsupervised, I ask one query: If it screws this up, can I undo it? If the reply is a wasted afternoon, run it free. If the reply is I am unable to take it again, the agent would not get close to it.
I discovered this one the embarrassing manner. I constructed a workflow that fired off emails quicker than I had ready the brakes. They weren’t offensive, simply not proper. “Cease it when it annoys me” works completely till one thing leaves the constructing, after which it would not work in any respect.
So, I wrote one arduous line the agent can’t cross. It by no means sends a message to a buyer, a accomplice or anybody with out my express approval. It hasn’t occurred since. Something that touches an actual human relationship or carries reputational weight, I keep within the room. AI is superb at sounding prefer it is aware of what it is doing, which isn’t the identical factor as really figuring out. The hole between these two is strictly the place an unsupervised agent goes mistaken.
The identical logic applies to something irreversible, so do not give your agent admin entry to your GitHub repository, as a result of a foul learn is recoverable however a foul write is not.
AI is superb at sounding prefer it is aware of what it is doing, which isn’t the identical factor as really figuring out.
Watch the cash and the API keys
The failure mode no person costs in is the invoice. Token pricing remains to be artificially low cost. That will not final, and when it stops, it would cease very noticeably. An agent caught in a loop can burn by means of 1000’s of {dollars} in API calls earlier than you’ve got seen.
Cap the spend wherever the tooling permits you to. Give each agent its personal devoted API key, reasonably than one shared key sitting throughout a number of workflows, and rotate them commonly. A static key you by no means contact is a door left completely open, and the longer it sits there unchanged, the extra publicity you are carrying with out realizing it.
Handle AI brokers as when you employed them
You would not hand a brand new rent the keys to the entire firm of their first week. Brokers are stranger than a brand new rent anyway, as a result of they work quicker and fail extra quietly, which suggests by the point you’ve got seen there’s an issue you are really conducting a panicked audit of all the things that occurred when you had been wanting elsewhere. Maintain the errors small and reversible, do not let something out the door with out you, and watch the meter such as you’re taxiing throughout city.
Get these proper, and an AI agent will get genuinely near a chief of workers. Although I am nonetheless not satisfied some quarterly updates had been ever meant to double as a sleep assist.
Governing 5 brokers is a evaluate course of. Governing 500 brokers is an infrastructure drawback.
Handbook evaluations and team-level approvals work when a handful of brokers are seen and intently watched. As soon as brokers unfold throughout enterprise items, instruments, and environments, that oversight breaks down.
Enterprises want an AI agent governance mannequin that features centralized identification, reusable insurance policies, and enforcement that holds throughout the entire agent workforce.
Key takeaways
At scale, AI agent governance should transfer from one-off approvals to centralized controls that maintain throughout each agent, staff, and setting.
Handbook evaluate breaks when brokers unfold throughout groups, instruments, knowledge sources, and environments.
Governing an agent workforce requires centralized agent identification, coverage propagation, and cross-environment enforcement.
AI agent governance groups want visibility into brokers, prompts, instruments, Mannequin Context Protocol (MCP) servers, knowledge sources, permissions, and runtime habits.
Enterprises ought to construct AI agent governance controls earlier than agent sprawl reaches manufacturing scale.
Why governance modifications because the agent workforce grows
A small variety of AI brokers will be ruled by means of direct evaluate. Groups can doc function, examine prompts, approve device entry, monitor utilization, and revisit an agent when one thing modifications.
The problem escalates because the AI agent workforce expands throughout enterprise items and methods. Think about a healthcare scheduling agent related to an digital well being file, appointment platform, and affected person communications system. One model could also be accredited to learn scheduling knowledge and ship reminders. One other could inherit broader entry, use an unapproved mannequin, or route protected well being data into the mistaken workflow.
Throughout dozens of brokers, a single permission change, device replace, or coverage hole can unfold earlier than anybody sees it.
The results lengthen far past governance operations. A small configuration error can expose delicate knowledge, disrupt providers, set off an audit, and pressure costly remediation throughout a number of methods. Because the agent workforce grows, groups should handle hundreds of relationships amongst brokers, instruments, knowledge, identities, insurance policies, and environments whereas maintaining controls constant because the system modifications.
The place guide governance breaks first
Governing an agent workforce ought to start throughout design and prototyping, earlier than brokers unfold throughout groups and manufacturing environments. Retrofitting identification, stock, coverage enforcement, and monitoring after deployment provides value, disruption, and management gaps.
The place governance breaks
What occurs at enterprise scale
What enterprises want
Stock
Brokers seem throughout groups, instruments, and environments with out a full file. For instance, a governance staff could got down to catalog 30 brokers and uncover 120 prototypes working in accredited platforms, notebooks, inner apps, automation instruments, and third-party providers.
A residing registry of each agent, proprietor, enterprise function, deployment setting, and related part.
Id
Shared credentials, broad service accounts, inherited human entry, and agent-to-agent handoffs make it troublesome to find out who acted and beneath what authority.
A novel identification for each agent, tied to scoped permissions, accredited instruments, knowledge entry, and enterprise function.
Coverage consistency
Groups interpret the identical rule in another way, and controls could apply in a single workflow or setting however not one other.
Central insurance policies that propagate throughout the agent workforce primarily based on danger, knowledge sensitivity, enterprise function, and setting.
Setting drift
Controls can weaken or disappear as brokers transfer by means of growth, staging, manufacturing, cloud, on-premises, or third-party platforms.
Cross-environment enforcement that retains identification, permissions, monitoring, and evaluate necessities intact all through the lifecycle.
What does governance infrastructure for an agent workforce want to incorporate?
Governance on the scale of an agent workforce requires infrastructure that manages particular person brokers and coordinates the system round them. An agent is sort of a machine on a manufacturing unit flooring: groups nonetheless want to examine it, tune it, change defective elements, and confirm that it operates safely.
At enterprise scale, upkeep is just a part of the job. Groups additionally must know the way every machine connects to the manufacturing line, which inputs it might probably use, which actions it might probably take, and the way the system responds when situations change.
For agent methods, which means governing prompts, instruments, MCP servers, vector databases, knowledge units, guardrails, APIs, downstream workflows, and predictive and generative fashions — together with the LLMs that energy agent reasoning — by means of a shared management layer.
Governance space
What groups want to regulate
Agent registry
Which brokers exist, who owns them, and the place they run
Agent identification
How every agent is authenticated, licensed, and tracked
Coverage propagation
Which guidelines apply throughout brokers, instruments, knowledge, and environments
Permission scope
What every agent can learn, write, replace, delete, or set off
Instrument entry
Which instruments, APIs, MCP servers, and workflows every agent can invoke
Element lineage
Which prompts, fashions, knowledge sources, and variations every agent makes use of
Runtime enforcement
Which actions are blocked, escalated, logged, or allowed
Monitoring
Which behaviors point out drift, misuse, value spikes, or coverage violations
Audit trails
What the agent noticed, chosen, referred to as, returned, determined, and did
Overview triggers
Which modifications require reapproval earlier than continued use
This infrastructure provides enterprises a sensible strategy to scale brokers with out counting on scattered spreadsheets, one-off approvals, or disconnected logs.
Three of those areas are price unpacking. Agent identification, coverage propagation, and cross-environment enforcement are what separate governance that works for one agent from governance that holds up throughout a whole lot of them.
How does centralized agent identification work?
You’ll be able to’t scope permissions, propagate coverage, or attribute actions with out first assigning each agent a sturdy, distinctive identification. Agent identification provides each agent a sturdy file and a managed strategy to act. That file ought to join the agent to its proprietor, enterprise function, danger tier, accredited instruments, knowledge entry, deployment setting, and evaluate historical past.
For instance, a procurement agent could examine vendor quotes and draft a advice whereas remaining blocked from approving purchases or altering provider data.
Id additionally separates person authority from agent authority. A human person could have entry to a system, however an agent appearing on that person’s behalf ought to nonetheless function inside its personal accredited scope.
Centralized identification additionally must persist throughout agent-to-agent workflows. When one agent delegates a job to a different, governance groups must know which agent initiated the handoff, what knowledge and directions moved with it, and what authority the receiving agent was allowed to train. Every agent ought to implement its personal permissions whereas the system preserves a hint of the total delegation chain. In any other case, a routine handoff can unexpectedly develop entry, drop an necessary constraint, or make accountability troublesome to reconstruct.
This distinction turns into vital at enterprise scale. When a whole lot of brokers act throughout methods and delegate work to at least one one other, safety and governance groups must attribute habits to particular brokers, detect anomalous entry patterns, hint handoffs, and revoke permissions with out disrupting unrelated workflows.
What’s coverage propagation and why does it matter?
Coverage propagation turns governance guidelines into reusable controls throughout the agent workforce. A coverage may outline which knowledge lessons an agent can entry, which instruments require human approval, which actions are prohibited, which logs have to be captured, or which environments can run high-risk workflows.
On the scale of an agent workforce, these guidelines needs to be utilized centrally and inherited by the proper brokers primarily based on danger tier, enterprise function, setting, and knowledge sensitivity. A high-risk HR agent, for instance, ought to inherit stricter evaluate, logging, and bias monitoring necessities than a low-risk inner documentation agent.
Coverage propagation additionally helps groups handle change. If a brand new regulatory requirement impacts brokers that course of private knowledge, governance groups ought to be capable of determine impacted brokers, replace the related coverage, apply it throughout environments, and confirm enforcement.
With out reusable coverage controls, every agent turns into its personal governance venture. That’s not solely exhausting for AI, safety, and governance groups; it additionally creates inconsistent enforcement, missed controls, and actual operational danger because the agent workforce grows.
How does cross-environment enforcement scale back manufacturing danger?
Cross-environment enforcement ensures that governance controls — identification, accredited scope, coverage necessities, monitoring guidelines, and audit expectations — transfer with an agent throughout growth, staging, and manufacturing, in addition to throughout cloud, on-premises, and third-party platforms.
Brokers don’t keep nonetheless: they hook up with new instruments, swap fashions, obtain immediate updates, and develop into new workflows.
That is particularly necessary for enterprises that run brokers throughout a number of clouds, on-premises methods, and third-party platforms. A governance program tied to just one deployment setting leaves gaps wherever brokers are constructed or deployed elsewhere.
Cross-environment enforcement ought to cowl entry, device invocation, parameter constraints, guardrails, logging, escalation, and evaluate triggers. It must also forestall unapproved modifications from silently increasing what an agent can do.
What leaders ought to ask earlier than agent development outruns the governance mannequin
Casual governance begins to pressure as brokers unfold throughout groups, environments, and enterprise processes. Earlier than development outruns the governance mannequin, leaders ought to verify that the group can reply these questions:
Do we have now a central registry of each agent and related part?
Does every agent have a named proprietor, enterprise function, and danger tier?
Does each agent have a novel identification with scoped permissions?
Can we implement reusable insurance policies throughout groups, environments, and deployment platforms?
Can we see which instruments, MCP servers, APIs, knowledge sources, and workflows every agent can entry?
Will we monitor prompts, fashions, instruments, vector databases, knowledge units, and retrieval sources as versioned parts?
Can we detect permission drift, coverage violations, retry loops, value spikes, and anomalous habits?
Can we reconstruct an agent’s resolution path, together with context, device calls, parameters, returns, and outcomes?
Do immediate, mannequin, device, workflow, or permission modifications set off reapproval?
Can we retire one agent and revoke its entry with out disrupting the broader agent workforce?
Weak solutions sign that agent development is outpacing the governance mannequin. Robust solutions give AI, safety, governance, and enterprise groups the management infrastructure required for manufacturing scale.
Govern your agent workforce earlier than scale turns into sprawl
Agentic AI can create actual enterprise worth, however manufacturing scale requires greater than structure and deployment. Enterprises want governance mechanics that maintain up when brokers unfold throughout groups, methods, and environments.
The shift from 5 brokers to 500 brokers modifications the job. Centralized identification, coverage propagation, cross-environment enforcement, monitoring, auditability, and lifecycle evaluate grow to be the working basis.
Agent workforce governance, generally referred to as AI agent governance, is the follow of managing many AI brokers by means of centralized controls for identification, possession, permissions, coverage enforcement, monitoring, auditability, and lifecycle evaluate.
Why are 5 brokers and 500 brokers completely different governance issues?
A small variety of brokers can usually be reviewed manually. A whole bunch of brokers require infrastructure for centralized identification, reusable insurance policies, cross-environment enforcement, runtime monitoring, and audit trails throughout the agent workforce.
When ought to enterprises begin planning for agent workforce governance?
Enterprises ought to begin throughout design and prototyping, earlier than brokers transfer into broad manufacturing use. Handbook evaluations, scattered inventories, and team-level coverage enforcement grow to be tougher to maintain as an agent workforce expands throughout groups and environments.
What ought to enterprises monitor for each AI agent?
What’s the greatest danger of an unmanaged agent workforce?
The most important danger is uncontrolled agent sprawl. Brokers could achieve unauthorized entry, function beneath inconsistent insurance policies, drift after system modifications, or take actions that groups can’t reconstruct after an incident.
The U.S. Cybersecurity and Infrastructure Safety Company (CISA) has ordered federal businesses to safe their methods by Saturday in opposition to ongoing assaults exploiting a crucial vulnerability within the Oracle E-Enterprise Suite (EBS) monetary software.
Found within the File Transmission element of EBS’s Oracle Funds product and tracked as CVE-2026-46817, this safety flaw permits unauthenticated risk actors with HTTP community entry to take over susceptible methods in low-complexity assaults.
Oracle launched safety updates to deal with the safety difficulty with its Might 2026 Essential Safety Patch Replace, urging prospects to patch their methods instantly.
“In some situations, it has been reported that attackers have been profitable as a result of focused prospects had failed to use accessible Oracle patches,” the corporate warned on the time. “Oracle subsequently strongly recommends that prospects stay on actively-supported variations and apply safety patches immediately.”
Whereas Oracle has not but flagged CVE-2026-46817 as exploited within the wild, risk intelligence firm Defused stated on June 29 that malicious actors had begun exploiting it within the wild.
“CVE-2026-46817 (CVSS 9.8 unauth HTTP takeover in Oracle E-Enterprise) is being exploited. Over the weekend, we noticed an actor exploiting the vulnerability on our Oracle E-Enterprise honeypots. This vulnerability has no identified earlier exploitation and no public POC code exists,” Defused famous.
Web safety watchdog Shadowserver now tracks over 1,000 Web-exposed Oracle EBS situations, greater than half of them in the USA. Nevertheless, there is no such thing as a info on what number of of them are honeypots or have already been secured in opposition to ongoing CVE-2026-46817 assaults.
On Wednesday, CISA additionally confirmed that hackers are actively exploiting the vulnerability, including it to its listing of identified exploited safety flaws, and ordering U.S. authorities businesses to patch susceptible Oracle EBS situations by Saturday, July 18, as mandated by Binding Operational Directive (BOD) 26-04.
“Oracle E-Enterprise Suite comprises an improper privilege administration vulnerability that enables an unauthenticated attacker with community entry through HTTP to compromise Oracle Funds. Profitable assaults of this vulnerability may end up in takeover of Oracle Funds,” CISA stated.
“Some of these vulnerabilities are frequent assault vectors for malicious cyber actors and pose vital dangers to the federal enterprise.”
Extra not too long ago, in June, it ordered them to safe their methods in opposition to a high-severity Oracle WebLogic Server flaw (CVE-2024-21182) that was patched two years in the past and is now actively exploited in assaults.
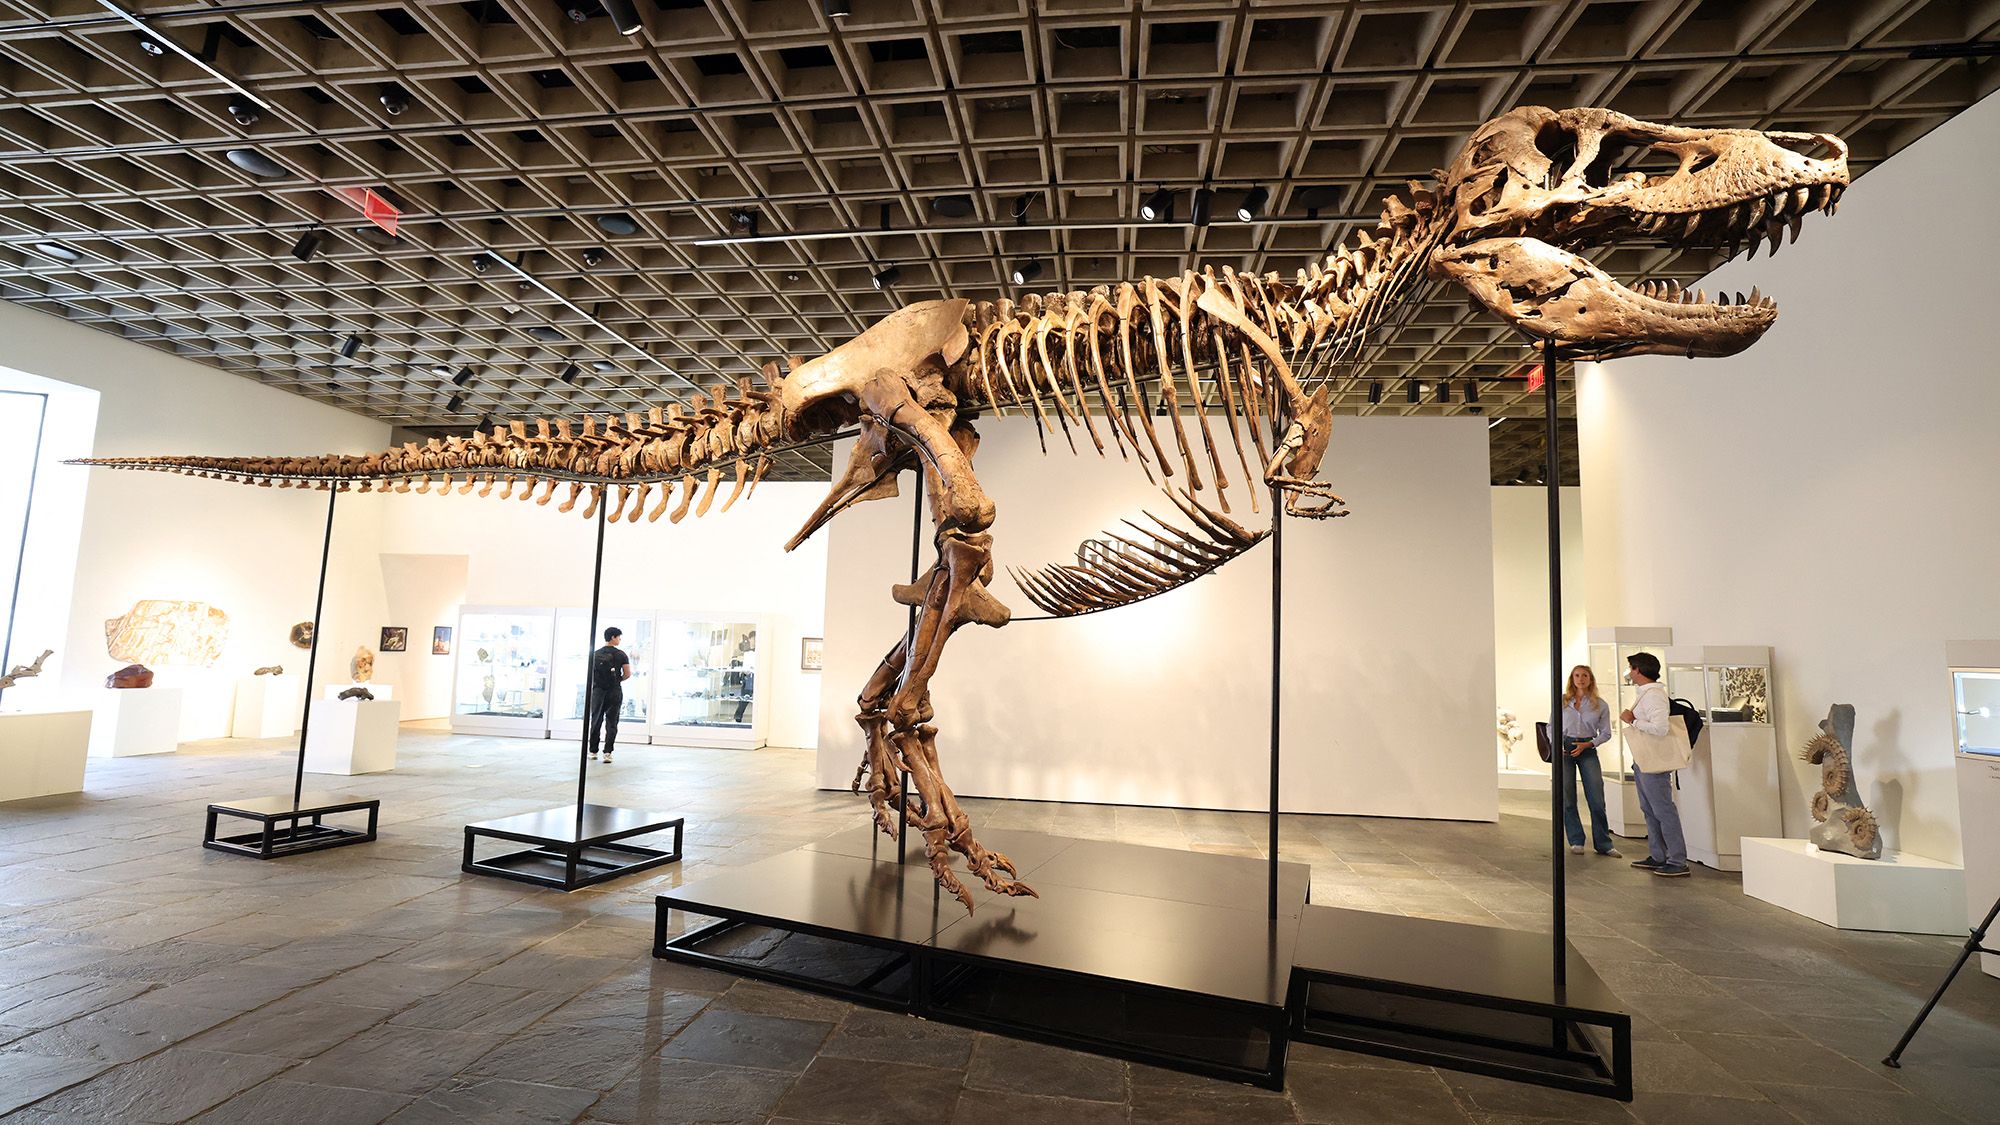
To paleontologists like me, nevertheless, a fossil like “Gus” — excavated from the Hell Creek Formation in South Dakota over three years beginning in 2021 by industrial collector Thomas Heitkamp and his crew — is just not a trophy or a murals. It’s an irreplaceable scientific archive. Fossils protect proof of evolution, extinction, progress, illness, harm and historical ecosystems. They’re finite, nonsubstitutable information of life’s historical past on Earth.
Science relies on unbiased verification of claims and wholesome debate. Researchers should have the ability to revisit specimens, take a look at earlier conclusions and ask new questions.
Newest Movies From
However as soon as a scientifically necessary fossil enters a personal assortment, entry for researchers is not assured. Collectors sometimes sequester their fossils of their properties. Even when privately owned specimens are loaned to museums, the house owners can change their minds, ending entry at any time. This subject is particularly of notice on the subject of Tyrannosaurus rex; a 2025 research discovered that whereas there have been 61 T. rex fossils in public trusts at the moment, 71 had been privately held.
That’s the reason the Society of Vertebrate Paleontology, of which I am a long-term member and president-elect, has lengthy argued that scientifically important vertebrate fossils belong within the public belief, curated in museums and universities that protect them completely, make them out there for analysis and share them with the general public.
Discovering a fossil
Supporters of economic fossil gross sales typically argue that with out gross sales to non-public collectors, specimens like “Gus” would stay buried or erode away. They’re proper about one factor: Discovery issues. Many extraordinary fossils have been discovered by ranchers, hikers, novice collectors and industrial excavators. Paleontology is accessible to everybody who has a watch for observing nature — you do not should be an knowledgeable with tutorial credentials to make an necessary discovery.
Fossil kits are bought on Amazon and different on-line retailers, encouraging curiosity in budding paleontologists.
(Picture credit score: Amazon)
However discovery is barely the start. A fossil’s scientific worth relies on cautious documentation of the place it was discovered, the rocks surrounding it, and the vegetation and animals preserved alongside it. These particulars enable scientists to reconstruct historical ecosystems, perceive how an animal lived and died, and interpret how its stays grew to become fossilized. When that contextual info is incomplete or misplaced, a lot of the fossil’s scientific worth is misplaced as properly.
Get the world’s most fascinating discoveries delivered straight to your inbox.
But even discovery, excavation and publication barely scratch the floor of a fossil’s scientific significance. The best scientific worth of a specimen typically comes many years later, when researchers ask new questions and apply new applied sciences that earlier generations by no means imagined. A specimen that appears absolutely studied right this moment might yield stunning new info tomorrow, however solely whether it is nonetheless out there for research.
Delayed discoveries
Contemplate the long-lasting dinosaurs, together with T. rex, Triceratops, Diplodocus and Stegosaurus, first collected greater than a century in the past. Early paleontologists may describe their shapes however had no solution to dig deeper by peering contained in the bones. As a result of these specimens had been preserved in museum collections, later generations may revisit them with applied sciences that did not exist after they had been found.
Paleontologist Larry Witmer and his collaborators at Ohio College began utilizing CT imaging 20 years in the past to reconstruct the inner anatomy of historic dinosaur fossils with out damaging them, primarily based on how X-rays journey via specimens. Mind cavities, internal ears, air areas, nerves and blood vessels grew to become seen for the primary time, revealing how dinosaurs balanced, heard, smelled and perceived their world.
Extra not too long ago, molecular paleontologist Jasmina Wiemann and her collaborators have recognized chemical traces preserved in fossil bone, eggshell and pores and skin that reveal facets of dinosaur biology unimaginable even a technology in the past. Till now, paleontologists had no solution to know particulars about metabolic charges and replica or the colours of pores and skin, feathers and eggs.
A skinny part of a Diplodocus femur reveals the microscopic structure of the bone, preserving a file of the animal’s progress and life historical past.
(Picture credit score: Kristina Curry Rogers)
In my very own analysis I exploit microscopes to uncover the hidden tales preserved inside dinosaur bones and enamel. Skinny sections of fossil bones reveal that dinosaurs grew extra like mammals and birds than like outsized reptiles. Microscopic modifications to bones seize traces of historical scavenging, and tiny signatures deep inside child dinosaur bones point out the second of hatching.
None of those discoveries would have been attainable if the unique fossils had vanished into inaccessible personal collections.
Shared pure heritage, on the public sale block
Fossils usually are not static objects whose scientific worth is exhausted as soon as they’re described. Their worth grows as science advances, however provided that future researchers can proceed to look at the unique specimens.
In fact, typically dinosaur fossils are rescued from obscurity via buy and instant deposition or donation to pure historical past museums. A few of the world’s most necessary dinosaur fossils are accessible right this moment as a result of people, corporations or organizations with the means to accumulate extraordinary specimens acknowledged that they belong the place scientists can proceed to check them and the place future generations can study from them.
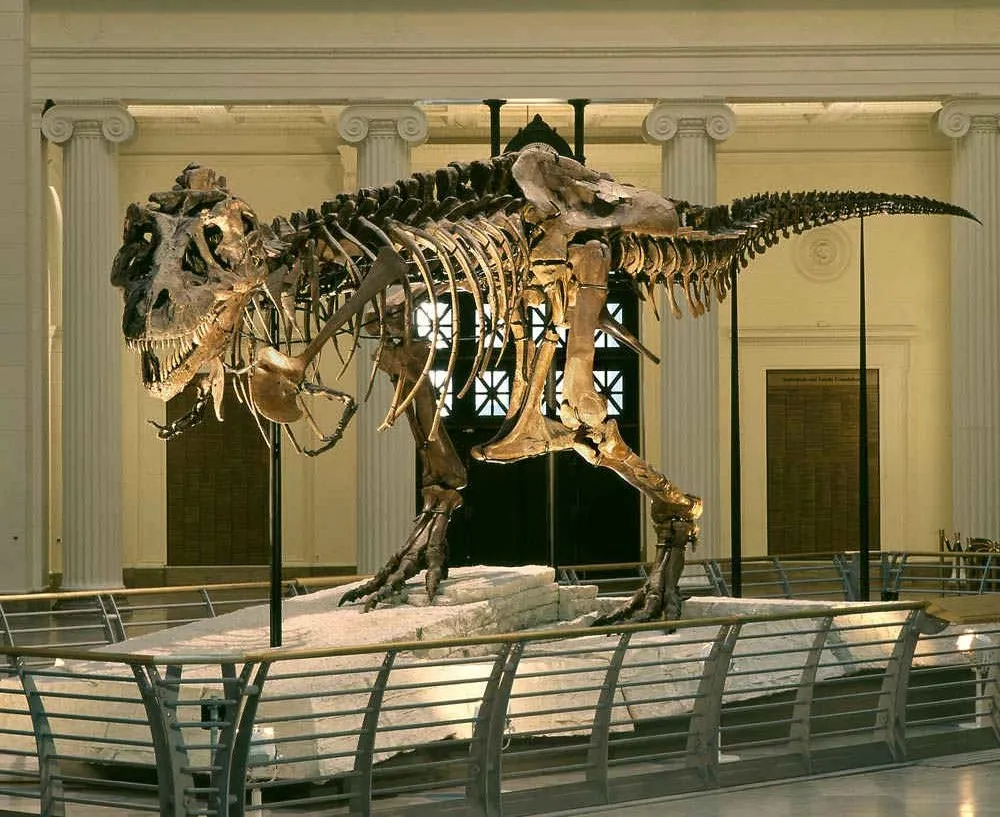
Schoolchildren had been among the many first to go to ‘Sue’ the T. rex as soon as it was displayed on the Discipline Museum of Pure Historical past in Chicago, Sick., because of funding from the California State College system, Walt Disney Parks and Resorts and McDonald’s.
(Picture credit score: copyright The Discipline Museum)
Buying a fossil in an effort to place it completely within the public belief is essentially totally different from buying it as a personal collectible: One expands entry, the opposite leaves entry unsure.
Dinosaurs belong to our shared pure heritage. They encourage surprise as a result of they join all of us to a world unimaginably older than our personal. For me, the query raised by auctions just like the one on July 14 of “Gus” is just not who can afford to personal these relics of the previous. It’s whether or not future generations have the prospect to check and study from them.
This edited article is republished from The Dialog beneath a Inventive Commons license. Learn the authentic article.
How a lot have you learnt concerning the king of the dinosaurs? Take a look at your information with our T. rex quiz!
Much like final time, What’s !essential #15 is fairly stacked — learn all about boundary-aware CSS, making grid lanes accessible, creating time-based net designs, fixing full-bleed CSS, bettering customizable , new net platform options, and extra.
Utilizing view() for boundary-aware CSS
Preethi Sam very expertly walked us via the idea of boundary-aware CSS. Utilizing view(), Preethi was in a position to create a spread of actually helpful results, a few of which I’ll share under:
I additionally wrote slightly one thing for the Grasp.dev weblog, about making interactive components invisible however accessible. It feels like extra work is required to make it totally accessible, and {that a} new worth for the hidden attribute could possibly be the reply.
Manuel Matuzović stated that it isn’t accessible (grid lanes structure, that’s, not Dan’s article, which is nice and will get straight to the purpose).
The right way to create time-based web site designs
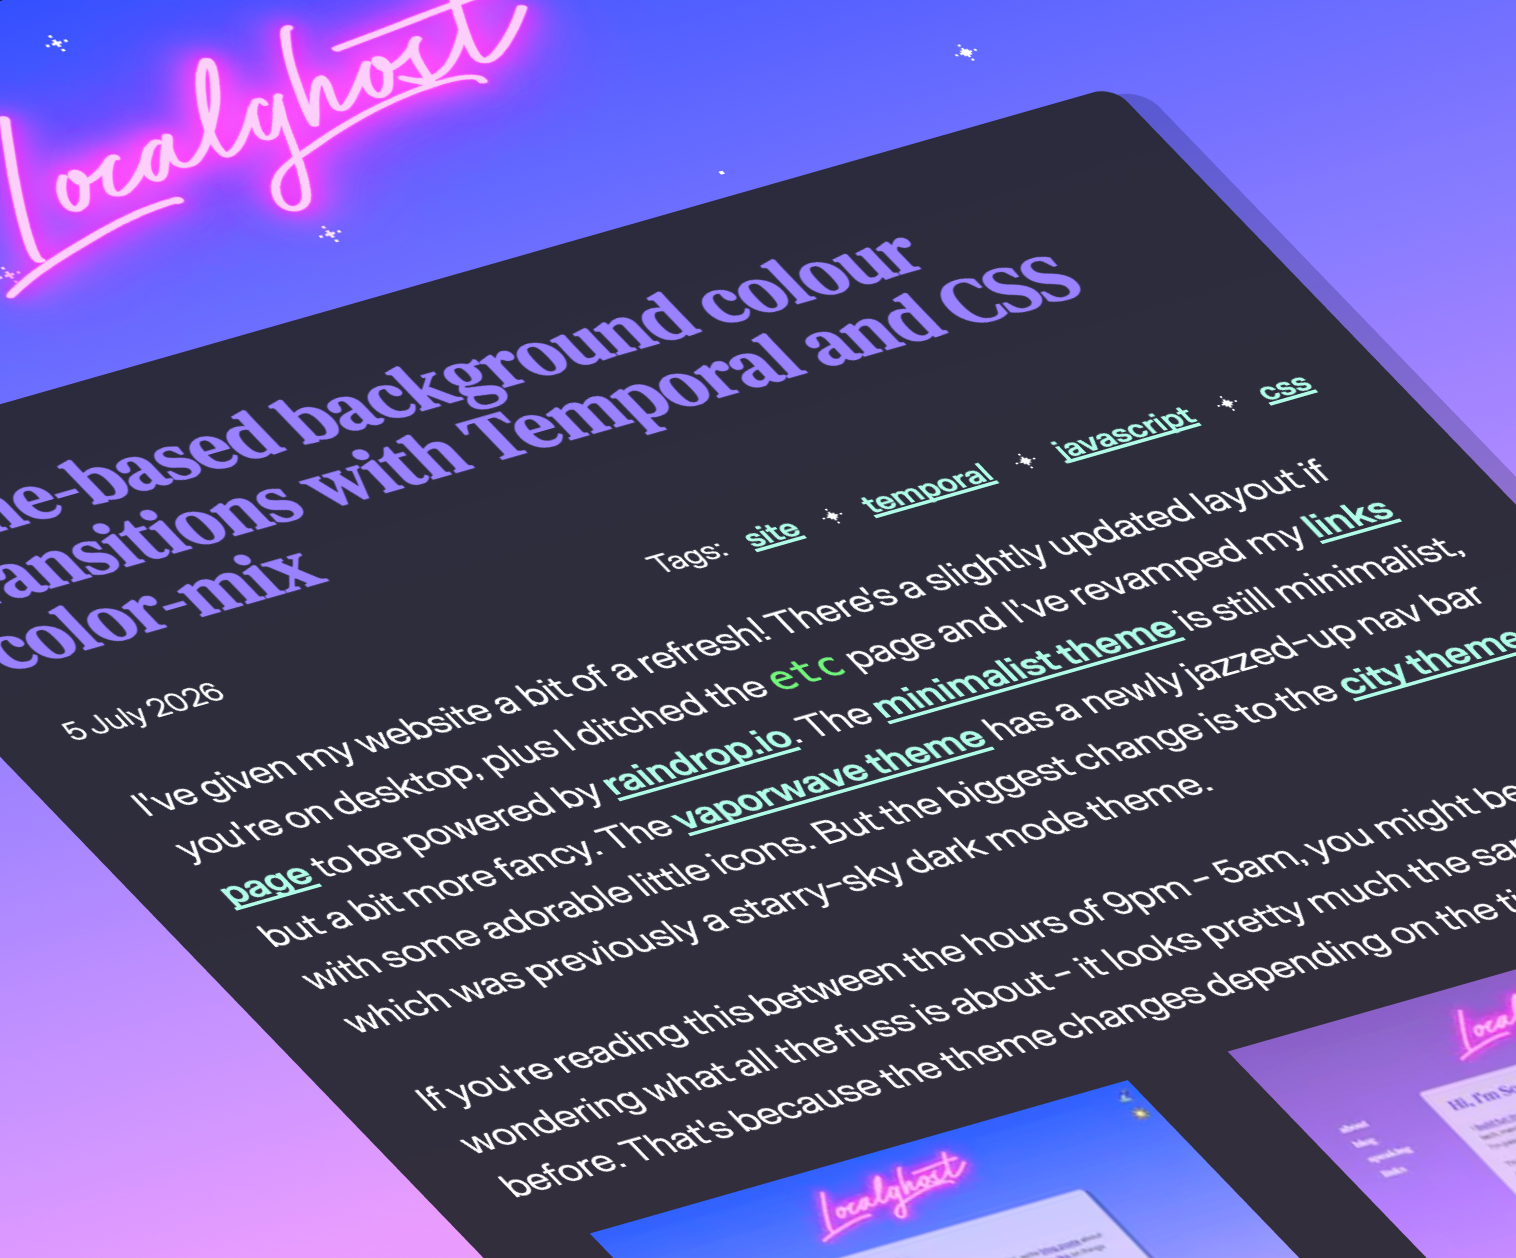
Sophie Koonin demonstrated make a web site change based on the time of day utilizing the Temporal API and color-mix(). Sufficient stated, that’s simply superior (like macOS’s dynamic wallpapers).
A repair for full-bleed CSS
David Bushell confirmed us repair full-bleed CSS. That’s, make one thing span the complete horizontal viewport (with none overflow — that’s the tough half!) regardless of being nested inside one other component. I simply like to see previous issues being solved with fashionable CSS (trace: it’s container question items).
And that’s why Declan Chidlow created FixCSS, which… nicely… fixes CSS in accordance with that. Now we are able to lastly swap border-radius (the Ethan Tremblay of CSS) for corner-radius. All is true with the world once more.
The right way to enhance customizable
Jake Archibald demonstrated enhance the UX of customizable s, addressing some sizing-related points. It’s a must-read for anyone excited about utilizing customizable .
By “new” I imply something from still-not-fully-supported-yet to just lately launched to imminent. Both method, right here’s Bramus and Una Kravets at Google I/O 2026 with 35 net platform options that you simply may not have heard of but or may wish to be reminded of:
Giant Language Fashions (LLMs) are more and more deployed to autonomously remedy real-world duties. A key ingredient for that is the LLM Operate-Calling paradigm, a broadly used method for equipping LLMs with tool-use capabilities. Nevertheless, an LLM calling capabilities incorrectly can have extreme implications, particularly when their results are irreversible, e.g., transferring cash or deleting knowledge. Therefore, it’s of paramount significance to contemplate the LLM’s confidence {that a} operate name solves the duty appropriately previous to executing it. Uncertainty Quantification (UQ) strategies can be utilized to quantify this confidence and stop doubtlessly incorrect operate calls. On this work, we current what’s, to our data, the primary analysis of UQ strategies for LLM Operate-Calling (FC). Whereas multi-sample UQ strategies, reminiscent of Semantic Entropy, present sturdy efficiency for pure language Q&A duties, we discover that within the FC setting, it presents no clear benefit over easy single-sample UQ strategies. Moreover, we discover that the particularities of FC outputs could be leveraged to enhance the efficiency of current UQ strategies on this setting. Particularly, multi-sample UQ strategies profit from clustering FC outputs primarily based on their summary syntax tree parsing, whereas single-sample UQ strategies could be improved by choosing solely semantically significant tokens when calculating logit-based uncertainty scores.
When you’re a Mac fan who’s at all times needed Lego to commemorate Apple’s most iconic Mac, your dream might quickly develop into a actuality. Lego just lately introduced that the proposal for an iMac G3 Lego brick set has formally moved to “Parking Lot” standing, the place the corporate is giving additional thought to its implementation earlier than deciding on manufacturing.
In August 2025, a fan named Terauma submitted a mock-up of the 1998 Bondi Blue iMac constituted of Lego bricks to Lego’s Concepts web site, the place followers might vote for the mission to maneuver ahead. Lego critiques concepts if a minimum of 10,000 followers vote for it.
The proposed set would include 700 items and wouldn’t solely recreate the turquoise-blue all-in-one (whose elements are clearly seen by the clear casing), but additionally the important equipment such because the round mouse, matching keyboard, and cables.
Lego’s overview board will now consider the proposal. Based on Lego, “Any Product Concept that wants further time after a overview spherical, for no matter cause, will probably be positioned into the Parking Lot till we are able to make a remaining determination.” On this case, the overview will doubtless embrace discussions with Apple, who would wish to grant Lego permission to do the mission.
Two years in the past, a proposed Apple Retailer Lego set made it to the Parking Lot however was finally dropped. Lego didn’t disclose why, however contemplating Apple’s historical past with the way it handles its model picture, the consensus that Apple denied a license in all probability isn’t far off. Primarily based on historical past, it doesn’t look good for the Lego iMac, however maybe a new incoming Apple CEO can have a change of coronary heart.
Within the mid-Nineties, Apple had fallen right into a disaster that threatened its very existence. The iMac is credited with saving the corporate. Though the ill-fated CEO Gil Amelio had initiated the iMac mission, it was accomplished by Steve Jobs upon his return to the corporate, and a younger British designer named Jony Ive. It was no coincidence that the iMac harkened to the 1984 Macintosh.
NASA is selecting up the tempo on its Artemis III mission preparations, urgent ahead on a number of fronts to assemble launch car {hardware} and starting routine simulations inside Artemis mission management.
The company is “full steam forward,” in line with a July 13 NASA replace. Throughout Kennedy House Middle (KSC) in Florida, elements of Artemis III’s House Launch System (SLS) rocket are coming collectively, present process exams and awaiting transportation for remaining integration forward of subsequent yr’s launch. NASA is focusing on mid-to-late 2027 for Artemis III, which is able to launch 4 astronauts into low Earth orbit (LEO) aboard the Orion spacecraft. It is going to be the second crewed mission of NASA’s Artemis program, which goals to determine a everlasting human presence on the moon.
Artemis III can be a vital stepping stone in NASA’s lunar touchdown structure, regardless of the mission not really flying to the moon. As an alternative, SLS will launch Orion and its four-person crew into LEO for rendezvous and docking operations with this system’s two business lunar lander automobiles: SpaceX‘s Starship and Blue Origin‘s Blue Moon spacecraft.
With the completion of the massively profitable Artemis II mission that flew astronauts across the moon in April and the second half of 2026 starting to depend down, NASA has shifted into full gear to finish meeting and testing of the {hardware} that can launch Artemis III.
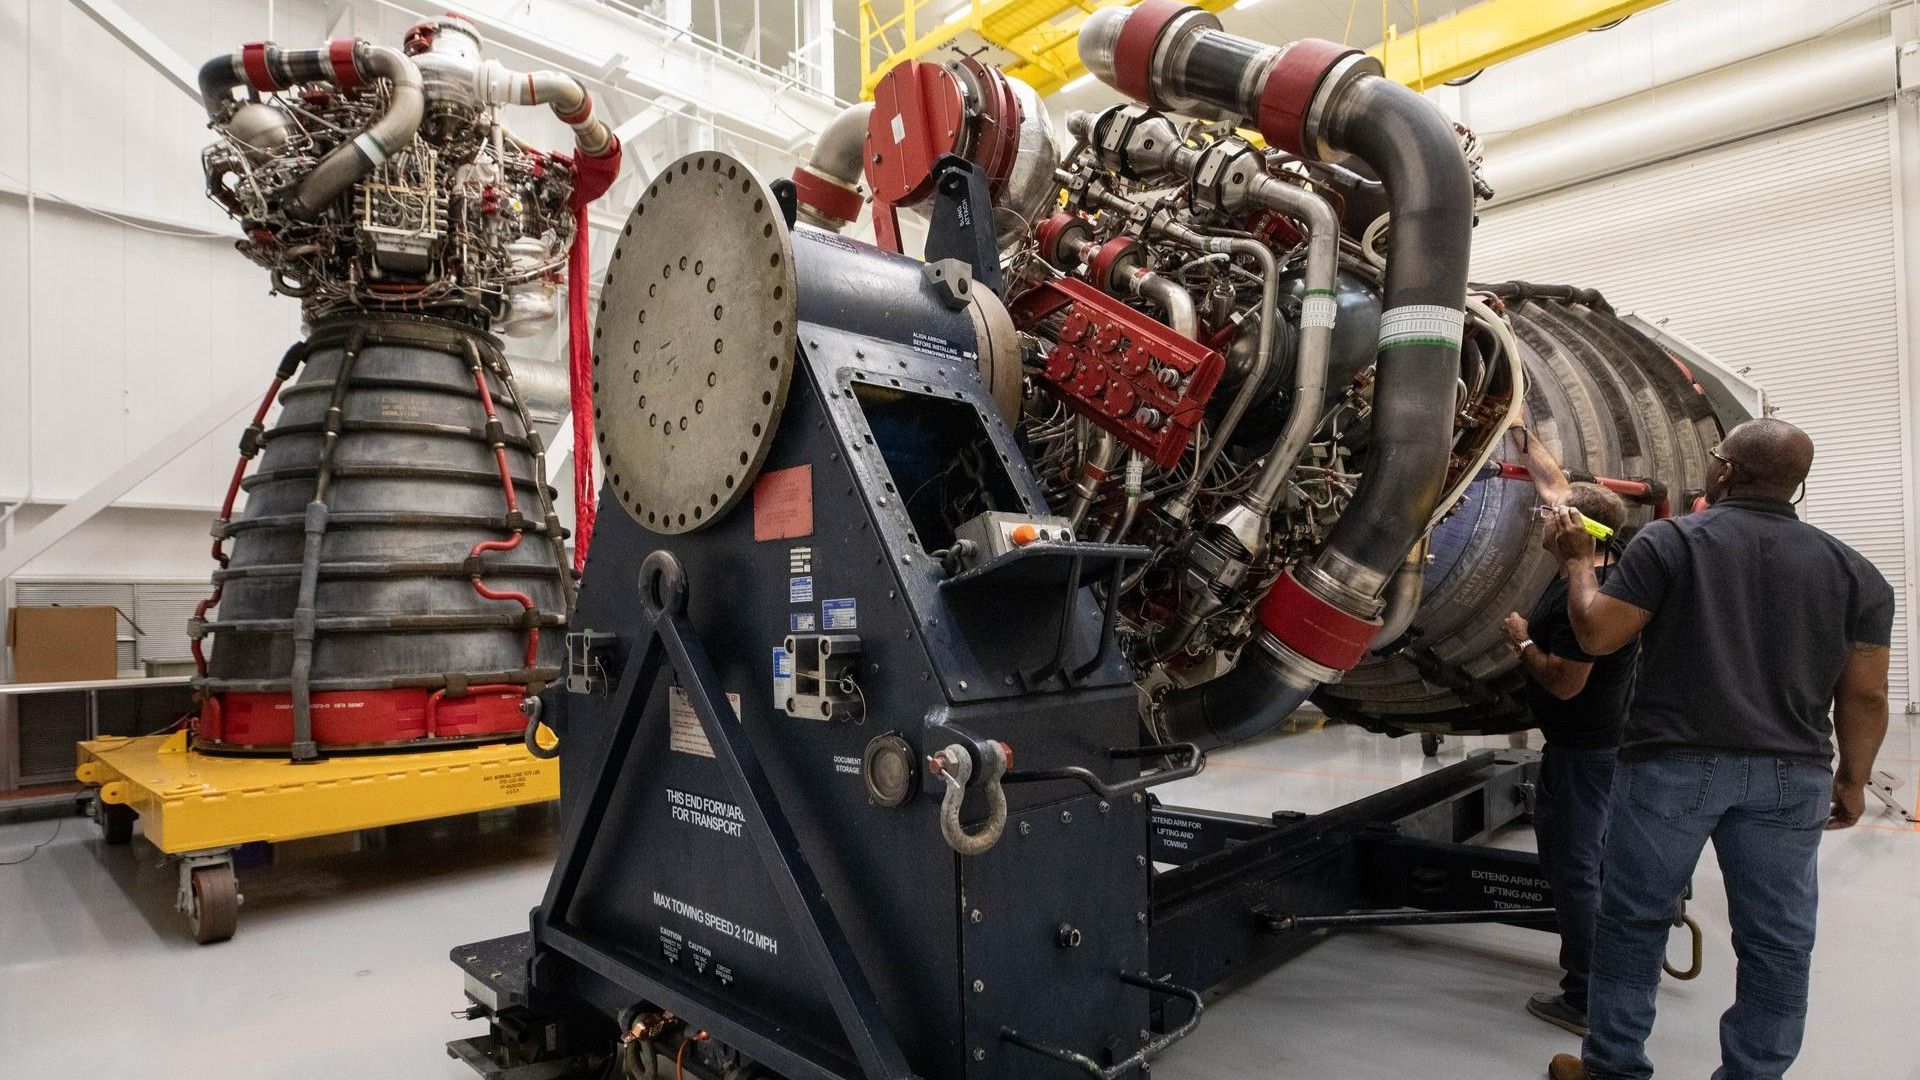
A number of elements for the mission’s SLS rocket have arrived within the Automobile Meeting Constructing (VAB) at KSC. The SLS core stage was delivered on the finish of April, and it was related with the rocket’s engine block part in Might. The primary two of the core stage’s 4 RS-25 engines arrived in June and can be put in on the SLS engine block as soon as the remaining two are delivered, after which NASA plans to start integration with the cell launch platform (MLP) and launch operations exams. A momentary climate cap was additionally delivered in June, which is able to shield the stage when NASA transports it to the launch pad for exams earlier than the total car is stacked.
The underside segments of each SLS strong rocket boosters (SRBs) had been delivered over the past week, and so they have been mounted on the MLP, in line with NASA’s replace. The higher SRB segments arrived at KSC through prepare in June and can endure inspection and testing earlier than the dual boosters are absolutely stacked.
Per NASA: Artemis launch director Charlie Blackwell-Thompson participates within the launch countdown simulation on July 2, 2026, in Firing Room 1 of the Launch Management Middle.
Picture credit score: NASA/Chad Siwik
Per NASA: Staff pose for {a photograph} following work contained in the VAB to safe the left-hand aft meeting strong rocket booster section to the cell launcher on the VAB on July 9, 2026.
Picture credit score: NASA/Ben Smegelsky
Per NASA: The left-hand and right-hand aft meeting strong rocket booster segments for NASA’s Artemis III SLS (House Launch System) rocket are secured to the cell launcher on the company’s Automobile Meeting Constructing at NASA’s Kennedy House Middle in Florida on July 11, 2026.
Picture credit score: NASA/Frank Michaux
Per NASA: Artemis III astronauts Randy Bresnik and Andre Douglas go to the Multi-Payload Processing Facility at NASA’s Kennedy House Middle on July 10, 2026.
Picture credit score: NASA/Cory Huston
Inside KSC’s Neil Armstrong Operations and Checkout Constructing, the Artemis III Orion is making important progress — engineers have now completed set up of the spacecraft’s warmth protect.
Artemis III would be the first Orion mission to make use of an upgraded warmth protect, that includes design enhancements gleaned from evaluation of sudden put on on the warmth protect flown on Artemis I. Orion’s service module can be at present contained in the Operations and Checkout Constructing and not too long ago accomplished acoustic testing. Each the service module and Orion capsule are actually being ready for becoming a member of and eventual transportation to the VAB for stacking.
The items for Artemis III are coming collectively at @NASAKennedy.The dual strong rocket boosters? They’re getting stacked.The launch group? They’re simulating the countdown.The warmth protect? It’s now connected to the Orion spacecraft.Full steam forward for Artemis III. pic.twitter.com/2f92kv6HEiJuly 13, 2026
On the personnel facet of issues, Artemis III group members at KSC have begun month-to-month launch simulation exams to hone procedures for SLS propellant loading, terminal depend operations (the ultimate 10 minutes previous to liftoff) and launch day operations. These exams will proceed recurrently main as much as Artemis III’s launch subsequent yr, in line with NASA.
As groups throughout NASA are busy readying all of the items for Artemis III, others are waiting for this system’s first lunar touchdown, deliberate for Artemis IV. That mission, scheduled for late 2028, will ship a crew of astronauts to the floor of the moon for the primary time since 1972. The SLS that can get them there’s additionally coming collectively piece by piece.
The liquid oxygen (LOX) tank for the Artemis IV SLS core stage was not too long ago relocated inside NASA’s Michoud Meeting Facility in New Orleans, positioning the tank for testing because it enters its subsequent section of manufacturing.
That is the primary in a three-part collection exploring how Cisco Disaster Response is partnering with nonprofit organizations which might be harnessing the ability of accountable AI in humanitarian settings. From assessing wants on the bottom to connecting affected individuals with data and providers, every installment examines a unique stage of the humanitarian response lifecycle — and the accountable AI ideas that should information the work at each step.
Within the preliminary hours and days of a humanitarian response, correct data is crucial and doubtlessly lifesaving. Aid organizations should transfer quick to get help to individuals in want, however earlier than they’ll act, they should perceive. Who has been affected? What do they want? The place are the gaps?
AI has the potential to expedite and remodel the way in which reduction organizations strategy wants assessments within the aftermath of an emergency. It may speed up knowledge assortment, floor insights quicker, and assist overstretched groups do extra with much less, finally facilitating the supply of humanitarian support to the individuals who want it. However in contexts the place individuals and communities are at their most susceptible, the necessity to leverage AI responsibly is paramount.
Cisco’s strategy to accountable AI
That rigidity between the big promise of AI and the necessity to deploy it responsibly is one thing we take severely at Cisco. Our strategy to accountable AI is grounded in six core ideas which might be embedded in how we work, how we innovate, and who we select to associate with. Once we help organizations working on the frontier of AI-enabled disaster response, we search for companions who maintain themselves to the identical requirements we do — and whose accountable AI commitments, in flip, assist inform and refine our personal.
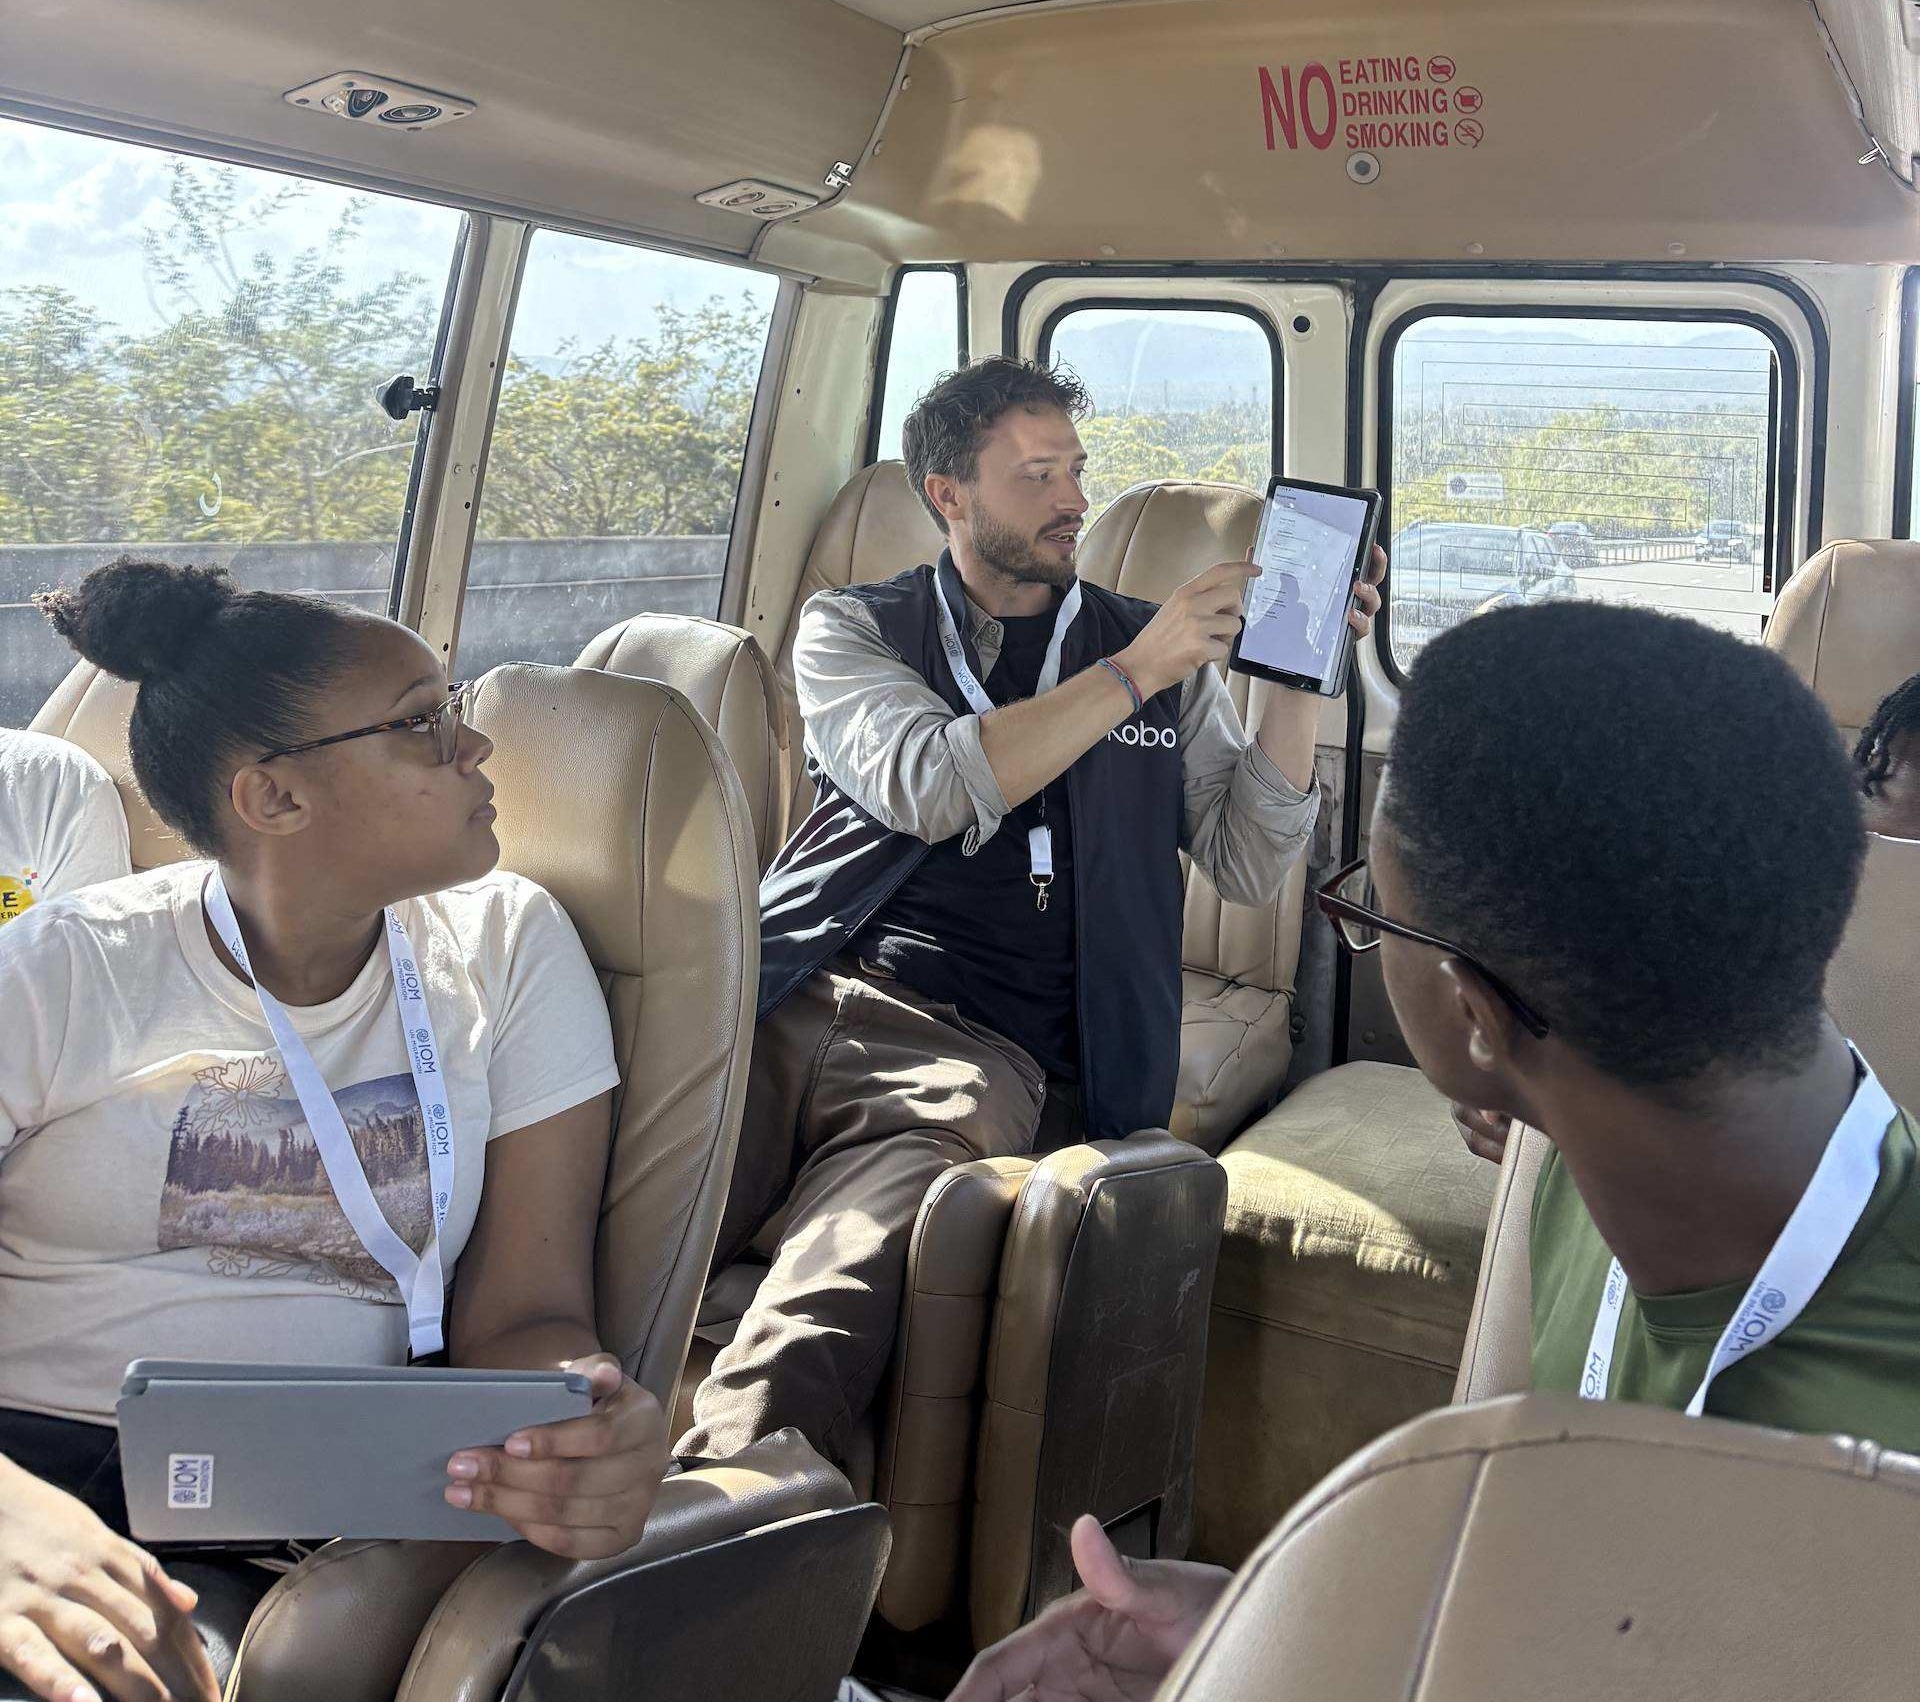
One such associate is Kobo, the group behind KoboToolbox: an open-source platform that greater than 35,000 organizations throughout 220 nations and territories depend on to design surveys, accumulate knowledge, and generate insights to tell packages and interventions in a number of the world’s most difficult environments. Cisco has partnered with Kobo since 2014, supporting the event of KoboToolbox into the versatile software program it’s in the present day — together with, most just lately, its early integration of qualitative evaluation options supported by massive language fashions. Now, with the KoboToolbox AI Formbuilder, the workforce is taking that one step additional: utilizing generative AI options to assist humanitarian organizations construct higher survey kinds quicker. By focusing each on potential good points and danger discount, these options allow humanitarian employees to expedite high-quality, high-volume knowledge assortment with out compromising on the safeguards wanted to guard each the information and the individuals it represents.
Operational challenges, moral questions: Why accountable AI issues
Cisco associate Kobo builds accountable AI-assisted instruments to assist reduction organizations collect knowledge rapidly and safely.
Humanitarian wants assessments type the spine of an efficient response. Discipline groups are sometimes working in harmful or distant situations, with restricted time and sources, gathering knowledge to know the complete scale and scope of what crisis-affected communities urgently want. Conventional knowledge assortment strategies like text-based surveys and paper kinds might be gradual, inconsistent, and liable to gaps or errors. And when the communities most affected by a disaster converse languages or dialects that aren’t effectively represented in these normal instruments, their voices danger being misplaced solely.
AI-assisted instruments have the potential to handle many of those challenges however, in doing so, they introduce new ones. The info collected in emergency settings — details about displaced youngsters and households, their places, their identities, their vulnerabilities — is very delicate. How do you steadiness the true impacts that may be achieved with the elevated velocity and effectivity of AI with the duty to deal with that knowledge safely and ethically?
Constructing higher humanitarian knowledge instruments with accountable AI on the core
Kobo’s strategy addresses these challenges by prioritizing the mixing of accountable AI capabilities straight into the information assortment workflow and the software itself. Options like automated speech-to-text transcription and AI-assisted translation permit discipline groups to seize detailed observations in actual time, within the languages spoken by affected communities. AI-powered type constructing helps even non-expert customers design high-quality, contextually applicable surveys in minutes relatively than hours, that means reduction employees can collect extra actionable knowledge quicker than ever.
“At Kobo, our strategy to accountable AI begins lengthy earlier than the top person—from early architectural selections and neighborhood co-design, right down to deciding on fashions that meet the very best moral and privateness requirements,” says Tino Kreutzer, Kobo’s Chief Working & Innovation Officer. “Earlier than writing a single line of code, we assess potential dangers and take a look at mannequin reliability utilizing solely artificial knowledge. By internet hosting one of the best accessible open-weight fashions in our personal setting, we guarantee person knowledge is rarely shared or used for business coaching whereas sustaining extremely dependable efficiency.”
“Humanitarian knowledge wants robust safeguards. That’s why we prioritize moral ideas corresponding to accuracy, privateness, and reliability in all our work.” – Tino Kreutzer, Chief Working & Innovation Officer, Kobo
Critically, the software is constructed with human oversight at its core. By design, the “human-in-the-loop” mannequin requires customers to evaluate, edit, and confirm AI-generated transcripts and translations straight inside the platform earlier than any knowledge is acted upon — a deliberate design selection that displays the transparency and accountability required for the accountable use of AI. Moreover, all AI processing occurs inside KoboToolbox’s personal infrastructure, sustaining full knowledge sovereignty.
KoboToolbox’s AI options in motion
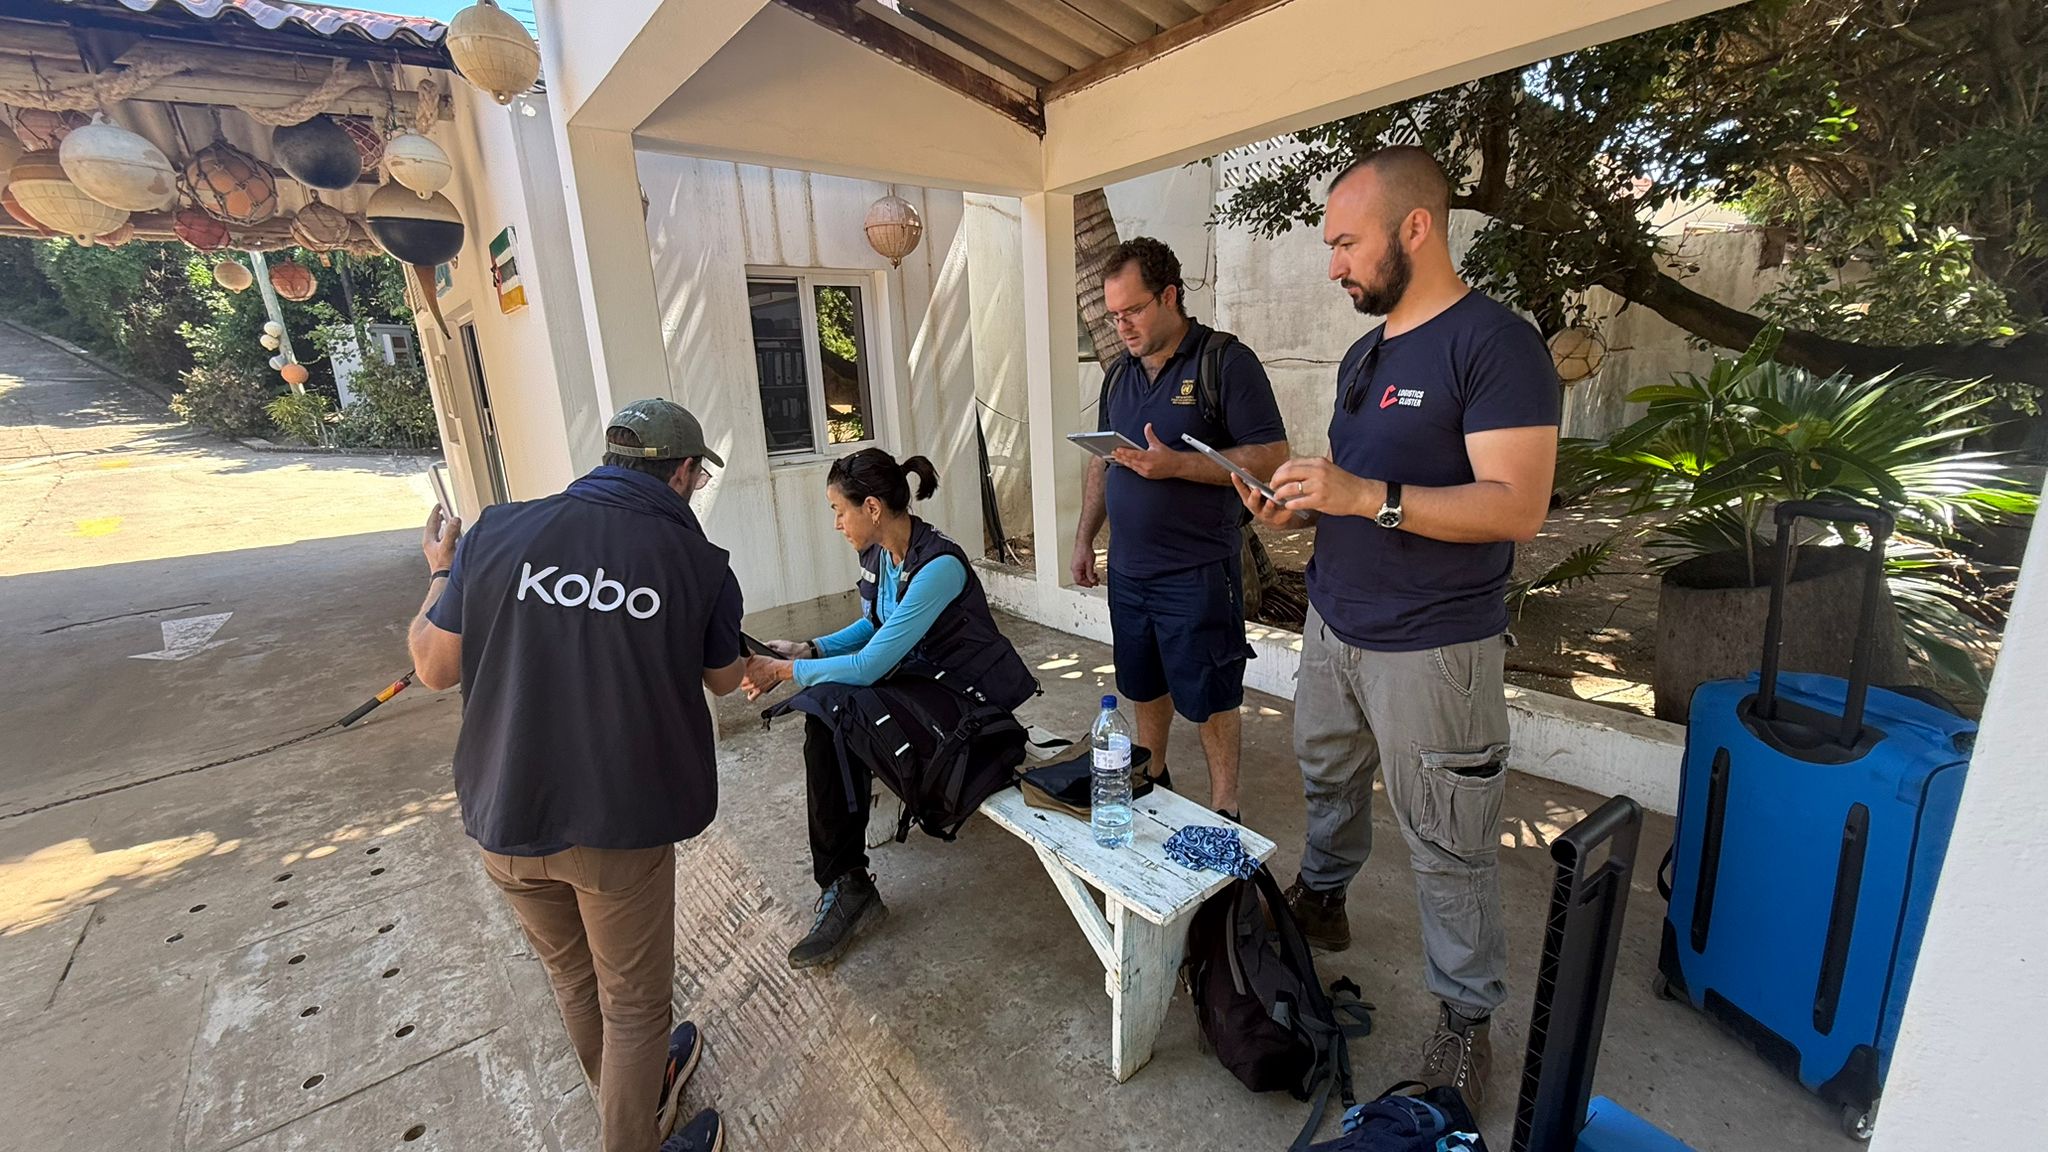
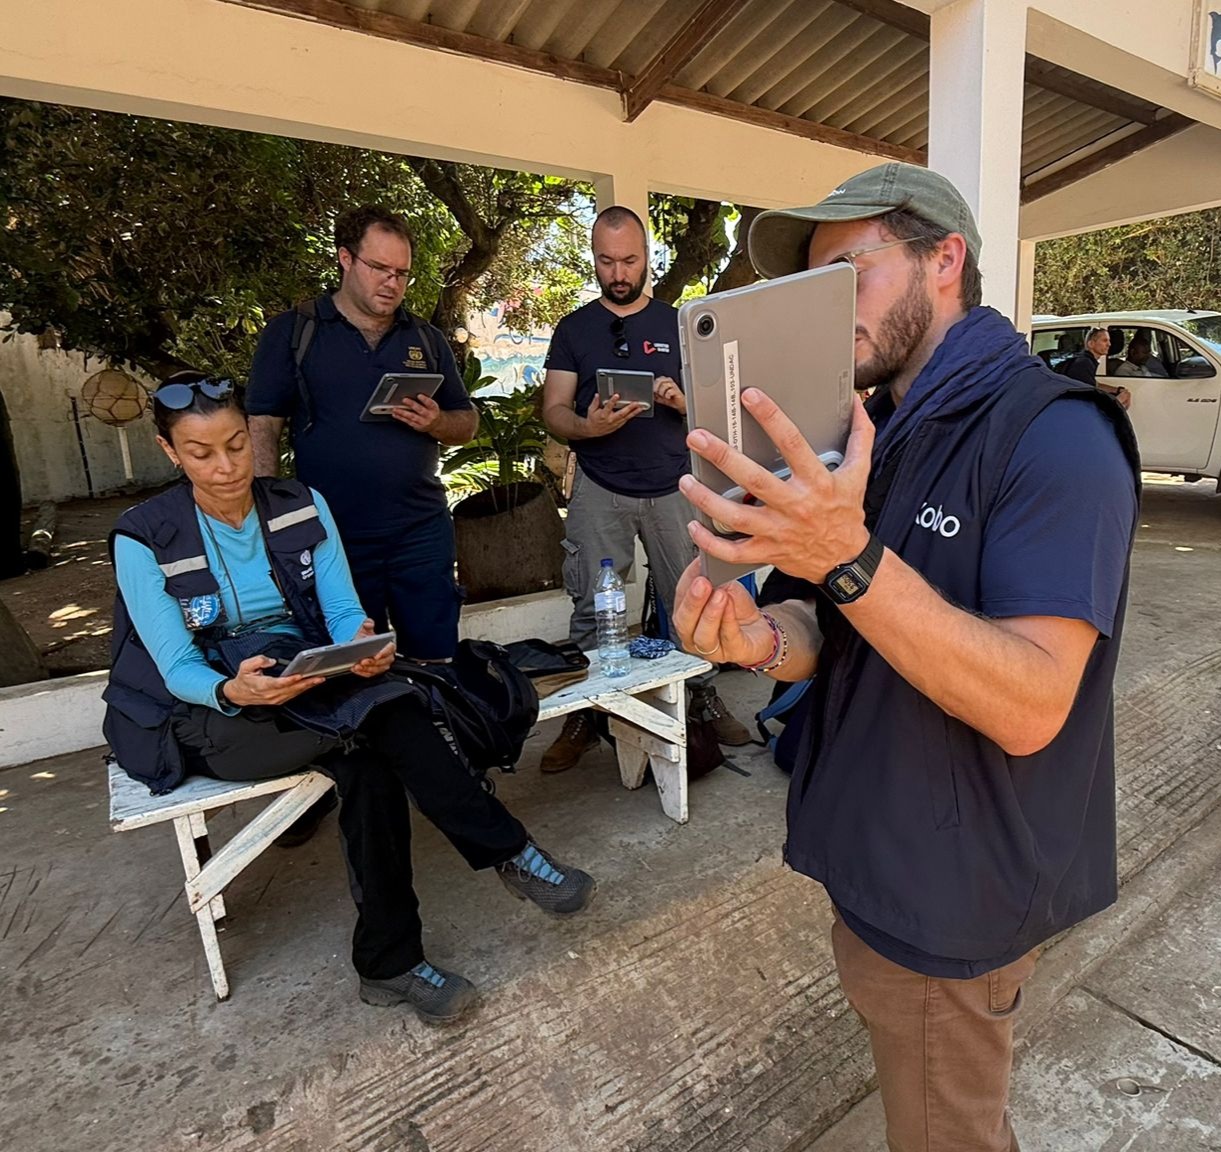
Kobo’s Joshua Beretta offering technical help through the Mozambique floods response in early 2026.
The proof for what this software may also help humanitarian organizations accomplish is already taking form. In a pilot with UN Girls throughout 14 nations within the Center East and North Africa, AI-powered transcription and translation options had been used to course of knowledge from greater than 14,000 individuals. The software considerably decreased the time required to transcribe and translate responses, and since all processing occurs inside KoboToolbox’s infrastructure relatively than being exported to exterior instruments, delicate knowledge stayed safe and inside the management of the organizations chargeable for it. For the reduction employees conducting interviews, that meant extra time being current within the conversations relatively than managing knowledge workflows — and the individuals being interviewed reported feeling genuinely heard consequently.
The instruments had been put to the take a look at in a sudden-onset emergency for the primary time in early 2026, when flooding in Mozambique displaced practically 700,000 individuals. Kobo deployed workers on the bottom to help frontline responders, the place a small workforce of enumerators used AI-assisted voice seize to file detailed observations about infrastructure situations and repair availability at lodging facilities for displaced households, producing richer, extra nuanced knowledge than conventional text-based strategies would have allowed. The total influence of that knowledge on the response continues to be being assessed, however the pilot validated that these instruments might be deployed responsibly beneath actual emergency situations.
The potential — and the obligations — of scaling accountable AI in humanitarian settings
The early outcomes recommend that AI might be responsibly deployed to enhance how reduction organizations perceive and reply to crises. Kobo is dedicated to protecting the software, together with these AI-assisted options, free or inexpensive for the 35,000+ organizations already counting on the platform. With that attain comes the potential to rework how humanitarian organizations conduct wants assessments at a worldwide scale.
“As we combine AI extra deeply into our work, we wish to guarantee we’re doing it in partnership with native organizations we work with, in ways in which assist meet the wants of the humanitarian sector with out inflicting further hurt,” says Kreutzer. “Ethics and transparency ought to all the time be prioritized over single-minded effectivity good points — that’s our guideline.”
At Cisco, we consider that the potential to leverage AI as a pressure for good is huge, nevertheless it’s solely as robust because the ideas guiding its use. We’re proud to associate with organizations like Kobo that each inform and share in our dedication to mitigating the dangers whereas maximizing the alternatives that these rising AI applied sciences current in humanitarian settings, with out jeopardizing the mission — or the individuals — they’re constructed to serve.
Subsequent within the collection: When affected communities want dependable data on how and the place to entry help within the aftermath of a disaster, how can reduction organizations leverage AI-powered instruments assist present it — safely, precisely, and at scale?
Each Python codebase has this downside. A operate that begins small. Two branches, perhaps three. Then somebody provides a case, another person provides one other, and a yr later you’ve got bought 200 traces of if/elif/else that no person needs to the touch. Here is an instance:
And yeah, it really works. However it additionally breaks the Open/Closed Precept, which states that software program entities (lessons, modules, and features) must be open for extension however closed for modification. There’s a higher approach to deal with this downside: the registry sample. This text covers what the registry sample is, how you can construct it up from a five-line dictionary to a production-grade reusable class, and when it really earns its place in your code. So, let’s get began.
# The Downside With If-Else Chains
An extended conditional chain fails in a couple of particular methods:
It violates the Open/Closed Precept. New case, new edit to a operate that already labored. Yesterday’s examined code will get cracked open, retested, and reviewed once more. The unit of change must be “add a file,” not “modify the central dispatcher.”
It piles unrelated logic into one place. Say your cost dispatcher covers bank cards, PayPal, and crypto. Now three domains that don’t have anything to do with one another are sharing one operate. The elif ladder forces them to share a room anyway.
It scales badly. Each new department provides to the cognitive weight of the entire operate. Twenty branches is twenty issues to scroll previous each time you might be debugging department quantity three.
It can’t be prolonged from exterior. Ship a library with a hardcoded get_model() chain and your customers are caught. They can’t add their very own mannequin with out monkey-patching or forking. The logic is sealed shut.
The registry sample fixes all 4 by flipping the connection. As an alternative of the dispatcher realizing about each possibility, every possibility declares itself to the dispatcher.
What’s the registry sample?
It’s principally a central lookup desk that maps keys to things (features, lessons, cases), the place every object registers itself as a substitute of being hardcoded into some conditional. In Python, that lookup desk is nearly all the time a dictionary, and “registering” is normally performed with a decorator.
# Going From If-Else to a Dictionary
The smallest potential win is to swap the chain for a dictionary lookup. One step, and the linear scan is gone:
That is already a registry — only a hand-maintained one. Dispatch is O(1), the choices are introspectable with checklist(MODEL_REGISTRY), and the dispatcher by no means adjustments. One wart stays: each new mannequin nonetheless means enhancing the dict and importing its class on the prime of the file. You are able to do higher by letting every part register itself.
# Constructing a Decorator-Primarily based Registry
That is the model you will really use each day. Registration occurs in a decorator, so each operate or class declares its personal key proper the place it’s outlined:
PAYMENT_HANDLERS = {}

def register(payment_type):
    def decorator(func):
        PAYMENT_HANDLERS[payment_type] = func
        return func
    return decorator

@register("credit_card")
def charge_credit_card(quantity):
    return f"Charged ${quantity} to bank card"

@register("paypal")
def charge_paypal(quantity):
    return f"Charged ${quantity} by way of PayPal"

@register("crypto")
def charge_crypto(quantity):
    return f"Charged ${quantity} in crypto"

def process_payment(payment_type, quantity):
    handler = PAYMENT_HANDLERS.get(payment_type)
    if handler is None:
        elevate ValueError(f"Unknown cost kind: {payment_type!r}")
    return handler(quantity)
Have a look at what modified. The process_payment dispatcher is 4 traces, and it’ll by no means develop. Need Apple Pay? Write a brand new operate, slap @register("apple_pay") on it, put it in no matter file you want, and also you’re performed. No central checklist to edit. No merge battle. No reopening examined code. The handler sits proper subsequent to its personal key, which is strictly the place the subsequent reader will search for it.
# Constructing a Reusable Registry Class
After you have two or three registries mendacity round, you’ll get uninterested in rewriting the identical decorator boilerplate. Wrap it in a small class and also you get collision detection, higher error messages, and a clear API totally free:
class Registry:
    """A reusable name-to-object registry."""

    def __init__(self, identify):
        self.identify = identify
        self._registry = {}

    def register(self, key):
        def decorator(obj):
            if key in self._registry:
                elevate KeyError(
                    f"{key!r} already registered in {self.identify!r}"
                )
            self._registry[key] = obj
            return obj
        return decorator

    def get(self, key):
        if key not in self._registry:
            elevate KeyError(
                f"{key!r} not present in {self.identify!r}. "
                f"Accessible: {checklist(self._registry)}"
            )
        return self._registry[key]

    def __contains__(self, key):
        return key in self._registry

    def keys(self):
        return self._registry.keys()
Now use it to construct a text-processing pipeline pushed fully by config:
transforms = Registry("transforms")

@transforms.register("lowercase")
def to_lower(textual content):
    return textual content.decrease()

@transforms.register("strip")
def strip_whitespace(textual content):
    return textual content.strip()

@transforms.register("remove_digits")
def remove_digits(textual content):
    return "".be a part of(c for c in textual content if not c.isdigit())

# The pipeline is now simply information. It might come from a YAML file,
# a CLI argument, or a database row.
pipeline = ["strip", "lowercase", "remove_digits"]
textual content = "  Order #4521 CONFIRMED  "

for step in pipeline:
    textual content = transforms.get(step)(textual content)

print(repr(textual content))

Output:
'order # confirmed'
That is the place the sample pays for itself. The habits of this system is now described by information — an inventory of strings — not by code. Reordering the pipeline, including a step, or handing the entire thing to a non-programmer by way of a config file all change into trivial.
# Auto-Registering Lessons With __init_subclass__
When your registry holds lessons as a substitute of features, Python has an excellent slicker trick. The __init_subclass__ hook (out there since Python 3.6) fires robotically each time a subclass is outlined, so subclasses register themselves with no decorator in any respect:
class DataLoader:
    _registry = {}

    def __init_subclass__(cls, fmt=None, **kwargs):
        tremendous().__init_subclass__(**kwargs)
        if fmt:
            DataLoader._registry[fmt] = cls

    @classmethod
    def get_loader(cls, fmt):
        if fmt not in cls._registry:
            elevate ValueError(
                f"No loader for {fmt!r}. "
                f"Accessible: {checklist(cls._registry)}"
            )
        return cls._registry[fmt]

class CSVLoader(DataLoader, fmt="csv"):
    def load(self, path):
        return f"Loading CSV from {path}"

class JSONLoader(DataLoader, fmt="json"):
    def load(self, path):
        return f"Loading JSON from {path}"

class ParquetLoader(DataLoader, fmt="parquet"):
    def load(self, path):
        return f"Loading Parquet from {path}"

loader = DataLoader.get_loader("parquet")
print(loader.load("gross sales.parquet"))   # Loading Parquet from gross sales.parquet
No decorator anyplace. Subclassing DataLoader with a fmt= argument is sufficient to register the brand new class. That is how numerous frameworks construct their plugin techniques below the hood.
# The place the Registry Sample Is Helpful in Apply
This isn’t an instructional train. It’s the spine of instruments you already use.
Machine studying experiment configs.Hugging Face Transformers, Detectron2, and MMDetection all use registries so you’ll be able to decide a mannequin, optimizer, or augmentation by string identify in a YAML file. build_model({"mannequin": "resnet50"}) beats an enormous if spine == ... block, and it lets researchers add architectures with out ever touching the coach.
File format and parser dispatch. Map extensions like "csv", "json", and "parquet" to loader lessons. Supporting a brand new format turns into “write one class,” not “edit the loader.”
Internet framework routing.Flask‘s @app.route("/customers") and Click on‘s @cli.command() are registries in disguise. The decorator maps a URL or command identify to the operate that handles it.
Plugin architectures. Any “drop a file on this folder and it simply works” system — whether or not pytest fixtures, Airflow operators, or serializer backends — is nearly all the time a registry amassing elements at import time.
Occasion handlers and state machines. Map occasion names or states to handler features as a substitute of branching on them. The transition desk turns right into a readable dictionary quite than a nest of conditionals.
# Sensible Concerns and Issues to Watch Out For
Registration solely occurs on import. A decorator runs when Python executes the file it lives in. In case your handlers sit in handlers/apple_pay.py and nothing ever imports that module, the @register decorator by no means fires and the handler quietly goes lacking. The repair is to verify registration modules get imported — normally by way of an specific import in a package deal’s __init__.py, or a small discovery loop with pkgutil.iter_modules that imports every thing in a plugin folder.
Guard in opposition to silent overwrites. With a plain dict, two elements registering the identical key clobber one another with no peep. Because the Registry class above reveals, elevating on a reproduction key turns a baffling runtime bug into an apparent error at import time.
Present individuals what is obtainable. At all times expose the keys with checklist(registry.keys()) and put them in your error messages. “Unknown mannequin: ‘lgbm’. Accessible: [‘logreg’, ‘random_forest’, ‘xgboost’]” saves way more debugging time than a naked KeyError.
Don’t attain for it too early. A registry is overkill for 2 or three steady branches whose logic genuinely differs. If the branches share no frequent signature, or the situations are ranges quite than discrete keys (if rating > 0.9 ... elif rating > 0.5 ...), a plain conditional is clearer. The registry wins in a single particular scenario: you might be dispatching on a discrete key to interchangeable behaviors, and also you count on that set of behaviors to develop.
# Wrapping Up
The registry sample trades a rising, central, hard-to-extend if/elif/else chain for a lookup desk that elements fill in themselves. The payoff is concrete. Your dispatcher stops altering. New options present up as new recordsdata as a substitute of edits to outdated ones. Conduct turns into one thing you’ll be able to drive from a config. And customers of your code get an actual extension level as a substitute of a locked door.
Begin small. Subsequent time you catch your self typing a 3rd elif identify == ..., cease and ask whether or not a dictionary would do. Normally it could. From there, the decorator and sophistication variations are a brief hop away.
# Earlier than
if sort == "a": ...
elif sort == "b": ...
elif sort == "c": ...

# After
@registry.register("a")
def handle_a(): ...
Your future self, scrolling previous a four-line dispatcher as a substitute of a 200-line ladder, will thanks.
Kanwal Mehreen is a machine studying engineer and a technical author with a profound ardour for information science and the intersection of AI with drugs. She co-authored the book “Maximizing Productiveness with ChatGPT”. As a Google Era Scholar 2022 for APAC, she champions variety and educational excellence. She’s additionally acknowledged as a Teradata Variety in Tech Scholar, Mitacs Globalink Analysis Scholar, and Harvard WeCode Scholar. Kanwal is an ardent advocate for change, having based FEMCodes to empower girls in STEM fields.