Home Blog Page 11

Some instruments and methods for hardening Home windows Server

0

[ad_1]

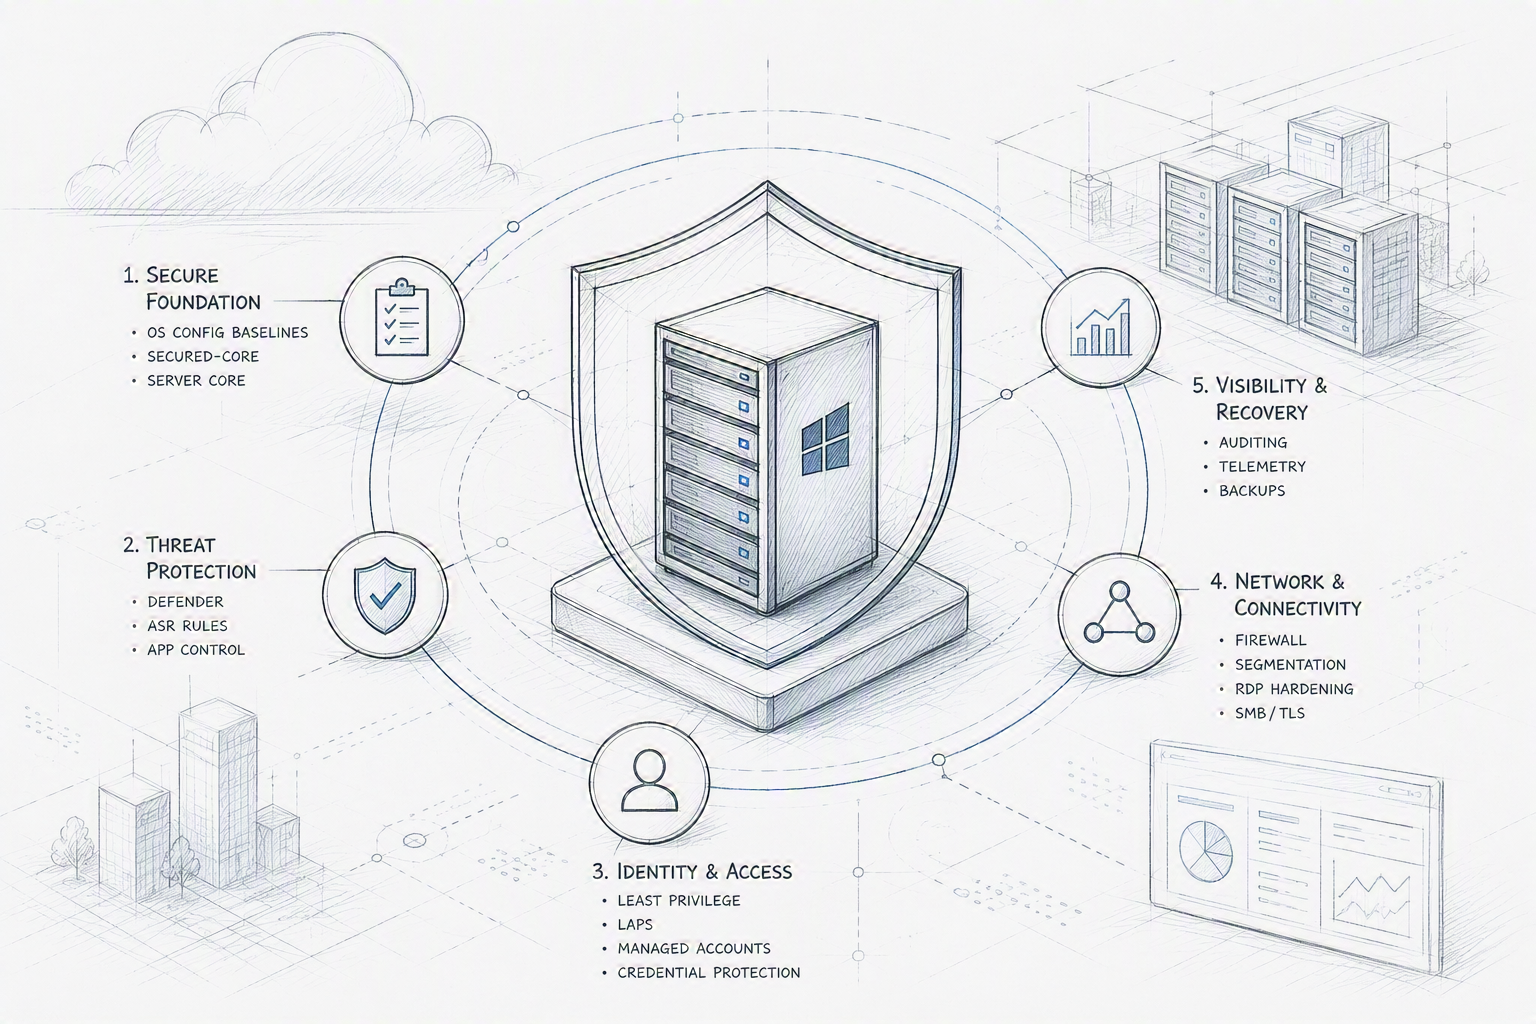
On this submit I’m going over some instruments and methods exist for hardening Home windows Server. As at all times, apply controls in keeping with the server’s function, check them towards consultant workloads earlier than manufacturing rollout, doc accepted exceptions, and preserve examined console and restoration entry in case a safety management impacts administration or utility compatibility.

Safety baselines flip a whole lot of particular person safety selections right into a constant, role-aware desired state. Utilizing OSConfig reduces publicity attributable to insecure defaults, legacy protocols, inconsistent administrator decisions, and configuration drift that attackers can exploit for credential theft, lateral motion, or persistence.

You should utilize use OSConfig at construct time to use the Microsoft safety baseline that matches the server function: SecurityBaseline/WindowsServer/2025/MemberServer, SecurityBaseline/WindowsServer/2025/DomainController, or SecurityBaseline/WindowsServer/2025/WorkgroupMember. The baseline comprises greater than 300 settings overlaying community publicity, credentials, lateral motion, persistence resistance, and auditing. It may be managed by PowerShell, Home windows Admin Heart, or Azure Coverage for Azure Arc-enabled servers.

You’ll be able to preserve OSConfig drift management enabled so unauthorized or unintentional adjustments are detected and corrected. Pilot the baseline with every workload, document required exceptions, and handle these exceptions centrally quite than weakening the baseline broadly.

Implementation steps: Establish the server’s function and the administration authority that may personal its settings, set up the OSConfig PowerShell module, assessment the matching situation, and apply it first to a consultant check server. Validate utility and administration entry, deploy the situation in managed rings, schedule and full the restart required after making use of the baseline, confirm the specified configuration and compliance outcomes, allow drift management, and document any accepted exceptions and restoration procedures.

Doable drawbacks: A baseline can disrupt legacy purposes, authentication strategies, community flows, or administration instruments that rely on weaker settings. Drift management may also reverse intentional emergency adjustments if they don’t seem to be recorded by the proper authority, so staged testing, documented exceptions, and examined restoration entry are important.

Documentation on Study: OSConfig safety configuration for Home windows Server | Deploy Home windows Server 2025 safety baselines with OSConfig | OSConfig safety settings repository

Home windows Server secured-core combines {hardware}, firmware, virtualization, and operating-system protections to ascertain belief earlier than Home windows begins and protect that belief whereas it runs. These controls mitigate bootkits, malicious or susceptible kernel drivers, direct reminiscence entry assaults, firmware tampering, and makes an attempt to extract credentials from the working system.

You deploy on {hardware} or digital machines that help TPM 2.0, UEFI Safe Boot, virtualization-based safety, DMA safety, and the opposite Secured-core necessities. Allow the OSConfig SecuredCore situation and confirm that Credential Guard, hypervisor-protected code integrity, kernel protections, and the signed boot chain are energetic.

It’s good to preserve system firmware, TPM firmware, hypervisor elements, and {hardware} drivers present. Take a look at older drivers earlier than enabling enforcement as a result of incompatible kernel drivers can stop security measures from activating or can have an effect on boot reliability.

Implementation steps: Affirm that the bodily server or virtual-machine platform meets the Secured-core necessities, replace firmware and drivers, and allow TPM 2.0, Safe Boot, virtualization extensions, and DMA or IOMMU safety within the platform configuration. Apply the OSConfig SecuredCore situation or configure the options by Home windows Admin Heart, restart as required, confirm that every safety is energetic, document proof of the {hardware} capabilities and working Home windows protections quite than solely the assigned coverage, and monitor for driver or workload compatibility points.

Doable drawbacks: Secured-core options require appropriate {hardware}, firmware, hypervisors, and signed drivers, which may enhance procurement prices or rule out older techniques. Virtualization-based protections can introduce a workload-dependent efficiency influence, and incompatible drivers or firmware may cause utility failures, characteristic activation issues, or troublesome boot restoration.

Documentation: What’s Secured-core server? | Configure Secured-core server | Home windows Server 2025 secured-core {hardware} necessities

Assault-surface discount removes code, providers, interfaces, and utilities that an attacker might exploit or misuse after gaining entry. A minimal Server Core deployment lowers the variety of vulnerabilities that require patching and reduces alternatives for interactive assaults, malicious searching, persistence, and abuse of pointless administrative instruments.

Set up Server Core except a supported workload particularly requires Desktop Expertise. Server Core has a smaller native interface and element footprint, lowering uncovered code, upkeep necessities, and alternatives for interactive misuse. Home windows Server 2025 cannot convert between Server Core and Server with Desktop Expertise after set up, so altering this selection later requires a clear set up.

Set up solely the roles, options, administration brokers, and utility elements required for the server’s objective. Take away out of date utilities and unused software program, keep away from searching the online from servers, and disable pointless providers solely after confirming function and utility dependencies. The place sensible, dedicate every server to a single safety or workload function.

Implementation steps: Affirm that the workload and vendor help Server Core, formally document the installation-option choice earlier than deployment, choose Server Core throughout set up, and outline the minimal roles, options, brokers, and software program required for the server’s objective. Set up solely these elements, configure distant administration and restoration entry, take away or disable unused elements after dependency testing, and confirm that the appliance, monitoring, backup, patching, and help processes nonetheless operate.

Doable drawbacks: Server Core could make native troubleshooting much less acquainted and will increase reliance on distant administration, automation, and command-line expertise. Some vendor purposes, help instruments, or directors require Desktop Expertise, and eradicating roles or disabling providers with out dependency testing can break workloads, monitoring, backup, or restoration operations.

Documentation: What’s the Server Core set up choice? | Server Core and Desktop Expertise set up choices

Patching and vulnerability administration establish and shut recognized weaknesses earlier than attackers can reliably exploit them. This observe reduces publicity to remote-code execution, privilege escalation, ransomware, susceptible drivers, compromised third-party elements, and assaults that focus on publicly documented vulnerabilities quickly after disclosure. Ensure you are conscious if any of your server workloads haven’t acquired the most recent safety updates deployed

Keep a list of operating-system, utility, driver, firmware, and management-agent variations. Use deployment rings to check updates rapidly, meet outlined remediation deadlines, set up out-of-band safety updates when required, and monitor replace compliance and pending restarts. Azure Replace Supervisor can present centralized evaluation and orchestration for Azure and Azure Arc-enabled servers.

Use Microsoft Defender Vulnerability Administration or an equal platform to find exposures, prioritize remediation by exploitability and enterprise influence, and confirm that fixes really take away the vulnerability. Patching Home windows whereas leaving internet-facing purposes, drivers, or firmware out of date doesn’t adequately harden the server.

Implementation steps: Stock servers and each supported replace supply, outline remediation deadlines and deployment rings, and configure Azure Replace Supervisor or one other actively developed orchestration platform. Home windows Server Replace Companies stays supported and out there however is deprecated and must be handled as a legacy choice quite than the popular platform for a brand new long-term design. Run vulnerability assessments, prioritize uncovered and actively exploited weaknesses, check updates, deploy them with coordinated reboots, confirm compliance after set up, and preserve rollback and exception procedures.

Doable drawbacks: Updates can require reboots, devour upkeep home windows, or introduce utility, driver, and efficiency regressions. Vulnerability scanners and administration brokers additionally devour assets and might generate false positives, so organizations want check rings, rollback procedures, upkeep coordination, and a risk-based course of for short-term deferrals.

Documentation: Azure Replace Supervisor overview | Cloud-native patch administration for Azure Arc-enabled servers | Microsoft Defender Vulnerability Administration | Deprecated Home windows Server options

Antivirus and endpoint detection and response mix prevention with behavioral monitoring and investigation. They mitigate malicious information, ransomware, internet and network-delivered payloads, suspicious course of exercise, persistence mechanisms, credential theft, and assaults that evade easy signature-based detection.

Run Microsoft Defender Antivirus in energetic mode except a documented and examined safety structure requires one other antimalware product. Allow real-time safety, conduct monitoring, cloud-delivered safety, computerized pattern submission, and frequent security-intelligence updates. Use the OSConfig Defender/Antivirus/WindowsServer/2025 situation because the beneficial Server 2025 configuration start line.

Onboard servers to Microsoft Defender for Endpoint or Microsoft Defender for Servers for endpoint detection and response, investigation, and centralized visibility. Allow tamper safety and preserve exclusions slender, workload-specific, and usually reviewed; broad path, course of, or extension exclusions create helpful hiding locations for attackers.

Implementation steps: Affirm licensing, connectivity, proxy, and third-party antivirus necessities, then apply the OSConfig Defender Antivirus situation or an equal centrally managed coverage. Allow real-time, conduct, cloud-delivered, sample-submission, and tamper protections; onboard the server to Defender for Endpoint or Defender for Servers; assessment Microsoft’s built-in, computerized server-role, and workload-specific exclusions earlier than including any guide exclusion; confirm sensor well being, signature forex, alert supply, and investigation entry; and periodically verify that each guide exclusion stays crucial.

Doable drawbacks: Actual-time scanning and endpoint telemetry can add CPU, reminiscence, disk I/O, community, and licensing prices, significantly on high-throughput workloads. False positives or quarantine actions can interrupt providers, whereas cloud-delivered capabilities can increase connectivity, privateness, or data-residency concerns; efficiency exclusions should subsequently be examined and stored narrowly scoped.

Documentation: Microsoft Defender Antivirus in Home windows | Microsoft Defender for Endpoint on Home windows | Defender Antivirus exclusions | Shield towards security-setting tampering

Assault floor discount guidelines stop high-risk behaviors quite than ready for a selected malicious file to be recognized, whereas community safety blocks entry to recognized or suspicious locations. Collectively they mitigate ransomware, credential theft, malicious scripts, abuse of trusted instruments, susceptible drivers, command-and-control site visitors, and payload supply.

Configure Microsoft Defender assault floor discount guidelines to dam frequent behaviors utilized by ransomware, credential theft, malicious scripts, susceptible signed drivers, and executable content material. Start with audit or warning mode, assessment telemetry for reputable workload dependencies, create narrowly scoped exclusions, after which transfer appropriate guidelines to dam mode on an outlined schedule.

Allow community safety the place supported to forestall processes from reaching malicious or untrusted locations. Handle these controls centrally by Group Coverage, Microsoft Defender for Endpoint safety settings administration, or one other supported coverage platform.

Implementation steps: Stock server workloads and make a rule-by-rule applicability choice for every server function quite than reusing a generic workstation ASR profile unchanged. Create a centrally managed ASR and network-protection coverage that originally makes use of audit or warning mode, accumulate and assessment occasions, verify business-critical dependencies, create narrowly scoped exclusions, transfer relevant guidelines to dam mode by deployment rings, confirm that protected purposes stay useful, and repeatedly assessment detections and exception use.

Doable drawbacks: ASR guidelines can block reputable automation, administrative instruments, installers, scripts, or line-of-business purposes that exhibit high-risk conduct. Audit mode can produce substantial telemetry, and broad exclusions can undermine the safety, so profitable deployment requires workload testing, occasion assessment, cautious exception design, and ongoing tuning.

Documentation: Assault floor discount capabilities | Consider Microsoft Defender Antivirus and ASR guidelines utilizing Group Coverage

Utility management adjustments the execution mannequin from permitting all the pieces besides recognized malware to permitting solely code that satisfies an accepted coverage. This system mitigates unknown malware, ransomware, unauthorized administrative utilities, malicious scripts, unapproved drivers, and opportunistic payloads that antivirus has not but labeled.

Use App Management for Enterprise to outline which executables, scripts, installers, libraries, and drivers might run. Home windows Server 2025 consists of OSConfig eventualities for Microsoft’s default coverage and utility blocklist. Begin in audit mode, accumulate Code Integrity occasion ID 3076, create required supplemental permit insurance policies, and transfer to enforcement solely after consultant workload testing. There are some good GUI instruments written by MVPs printed on GitHub that make this very straightforward. https://github.com/HotCakeX/Harden-Home windows-Safety

Monitor blocked-code occasion ID 3077 after enforcement and preserve a managed course of for coverage updates and emergency restoration. Utility allowlisting is considerably stronger than relying solely on malware signatures as a result of unapproved code is prevented from working even when it has not but been labeled as malicious.

Implementation steps: Confirm that the gadget is working a production-signed Home windows Server 2025 construct as a result of the OSConfig default coverage does not allow flight-signed binaries. Stock accepted purposes, scripts, drivers, publishers, and replace mechanisms, then deploy the default coverage and utility blocklist by OSConfig in audit mode. Accumulate occasion ID 3076, construct and deploy required supplemental insurance policies, and signal insurance policies solely when the extra tamper resistance is required and certificates lifecycle, coverage servicing, elimination, and offline restoration have been examined. Take a look at utility updates and restoration, transfer the coverage to enforcement in phases, and monitor occasion ID 3077 and coverage well being after deployment.

Doable drawbacks: Poorly designed insurance policies can block reputable purposes, updates, scripts, drivers, or boot-critical elements and might trigger a extreme service outage. Sustaining permit insurance policies creates operational overhead, particularly for continuously altering software program, and accepted instruments can nonetheless be abused, so audit-mode deployment, managed updates, and offline restoration procedures are crucial. Signed insurance policies present stronger tamper resistance however are deliberately more durable to take away, together with throughout restoration.

Documentation: Configure App Management for Enterprise through the use of OSConfig | App Management for Enterprise

A bunch firewall limits which techniques and purposes can talk with the server, even when upstream community controls are absent or bypassed. Restrictive guidelines cut back publicity to service exploitation, scanning, lateral motion, distant administration abuse, command-and-control site visitors, and unintentional publication of listening providers.

Allow Home windows Defender Firewall on Area, Non-public, and Public profiles. Retain the default block for unsolicited inbound site visitors and create solely the principles required by the server function. Scope guidelines by program or service, protocol, native port, distant deal with, interface, and profile quite than creating broad port-based or any-source exceptions.

Log dropped packets and profitable connections the place operationally acceptable, centrally monitor coverage adjustments, and assessment stale guidelines. Apply specific outbound restrictions to high-value or tightly managed servers the place possible, particularly when they need to talk with solely a small set of replace, identification, administration, and utility endpoints.

Implementation steps: Stock listening providers and required inbound and outbound flows, allow the firewall on all profiles, and create narrowly scoped guidelines for the server function. Resolve whether or not regionally created guidelines might merge with centrally deployed guidelines for every profile, confirm the efficient coverage on consultant servers, take away out of date or duplicate guidelines, check utility, area, cluster, backup, and administration site visitors, allow acceptable logging, deploy the coverage centrally, and monitor rule adjustments and blocked connections earlier than introducing selective outbound restrictions.

Doable drawbacks: Incorrect firewall guidelines can interrupt utility site visitors, clustering, area operations, monitoring, backup, or distant administration and might make analysis troublesome. Detailed connection logging consumes storage, whereas restrictive outbound insurance policies require steady upkeep as service endpoints change, so guidelines must be documented, examined, and deployed with restoration entry.

Documentation: Home windows Firewall rule suggestions | OSConfig baseline community protections

Distant administration exposes privileged authentication and interactive management paths which might be enticing targets for brute-force assaults, credential theft, session hijacking, and exploitation of internet-facing providers. Gateways, multifactor authentication, encrypted periods, restricted supply networks, and credential isolation cut back the probability {that a} stolen password or uncovered administration port leads on to server compromise.

Disable Distant Desktop Companies when it isn’t required. When it’s required, use a VPN or Distant Desktop Gateway, require multifactor authentication and Community Degree Authentication, prohibit supply networks and approved teams, use trusted TLS certificates, and configure wise idle and disconnected-session limits. Disable clipboard, drive, printer, port, and gadget redirection except the operational want outweighs the data-transfer threat.

Use Distant Credential Guard just for appropriate direct RDP administration of Lively Listing-joined targets utilizing Kerberos so credentials aren’t despatched to the distant host. Distant Credential Guard is not supported by Distant Desktop Gateway or Distant Desktop Connection Dealer. For helpdesk entry to a probably compromised host, use Restricted Admin mode as a substitute of Distant Credential Guard. By no means expose TCP port 3389 on to the web, and keep away from utilizing saved privileged credentials on abnormal administrator workstations.

Implementation steps: Disable RDP on servers that do not require it. For brokered or externally initiated entry, place RDP behind a VPN or MFA-protected Distant Desktop Gateway and prohibit permitted customers and supply networks. For appropriate direct RDP administration of Lively Listing-joined targets, configure Distant Credential Guard individually; use Restricted Admin mode for acceptable helpdesk eventualities. Configure Community Degree Authentication, trusted TLS certificates, session limits, and required redirection controls, check routine and emergency entry, and monitor distant logons and gateway exercise.

Doable drawbacks: Gateways, VPNs, MFA providers, and safe administrative hosts add licensing, infrastructure, and help dependencies, and their outage can block reputable administration. Gadget-redirection restrictions can hinder help workflows, whereas Community Degree Authentication and Distant Credential Guard are compatible and delegation limitations; a individually secured emergency entry path is subsequently required.

Documentation: Plan multifactor authentication for Distant Desktop Companies | Distant Credential Guard

Least privilege limits every identification and session to the minimal actions required for its activity. Separating normal and privileged accounts constrains the injury attributable to phishing, token or password theft, malicious insiders, susceptible administrative instruments, and compromised lower-trust units, whereas lowering alternatives for privilege escalation and persistence.

Give directors normal consumer accounts for routine work and separate privileged accounts for administrative duties. Reduce membership of native Directors, Area Admins, Enterprise Admins, and different highly effective teams; assessment membership and assigned consumer rights usually; and forestall extremely privileged identities from signing in to lower-trust servers and workstations.

Use Simply Sufficient Administration endpoints, Home windows Admin Heart role-based entry management, and time-limited elevation the place attainable. Delegate particular duties quite than granting unrestricted interactive or PowerShell entry, and preserve individually protected emergency accounts for identity-service outages.

Implementation steps: Stock privileged human accounts, service principals, managed identities, service and automation credentials, scheduled duties, native group membership, duties, and logon places. Create separate normal and administrative identities, take away pointless standing memberships, delegate duties by function teams, JEA endpoints, Home windows Admin Heart RBAC, or time-limited elevation, prohibit high-tier logons to secured administrative hosts, check that every function can carry out its accepted duties, and monitor privileged-group, function, automation, and emergency-account use.

Doable drawbacks: Designing roles, JEA endpoints, approval processes, and time-limited entry requires ongoing engineering and governance. Excessively slender delegation can delay troubleshooting or incident response, whereas separate accounts add friction for directors, so permissions must be examined towards actual duties and emergency entry ought to stay tightly managed however usable.

Documentation: Simply Sufficient Administration | Home windows Admin Heart consumer entry choices | Enterprise entry mannequin

Home windows LAPS replaces shared or manually maintained native administrator passwords with distinctive, random, mechanically rotated credentials. It mitigates password reuse, pass-the-hash assaults, credential dumping, and broad lateral motion through which compromise of 1 server’s native administrator credential grants entry to many others.

Use Home windows Native Administrator Password Resolution to assign a novel, random, mechanically rotated native administrator password to each server. The backup vacation spot is dependent upon be part of state: Lively Listing-only units can use solely Lively Listing, Microsoft Entra-only units can use solely Microsoft Entra ID, and hybrid-joined units can use both vacation spot however not each concurrently. Tightly prohibit and audit password retrieval, configure password historical past and post-authentication rotation, and monitor policy-processing failures.

By no means reuse a standard native administrator password throughout servers as a result of one compromised password or hash can allow broad lateral motion. OSConfig offers the LAPS/WindowsServer/2025/MemberServer situation for member servers. Workgroup techniques will be managed by LAPS for Azure Arc, which Microsoft presently paperwork as a preview characteristic. On area controllers, use Home windows LAPS to handle the Listing Companies Restore Mode password the place acceptable.

Implementation steps: Choose the password-backup vacation spot permitted by the gadget’s be part of state, put together Lively Listing or Microsoft Entra ID, and establish the native account to handle. For workgroup techniques, consider the operational and help implications of the preview LAPS for Azure Arc service earlier than adoption. Configure password size, complexity, age, historical past, and post-authentication actions by coverage or OSConfig; configure DSRM password administration for relevant area controllers; delegate password learn and reset permissions to a small accepted group; pilot the coverage; confirm password backup and rotation; check approved restoration; and monitor LAPS processing and retrieval occasions.

Doable drawbacks: LAPS introduces listing, coverage, permissions, auditing, and restoration dependencies that should be designed accurately. Scripts or purposes that depend on a hard and fast native password can fail, password rotation can disrupt energetic periods or automation, and overly broad rights to retrieve saved passwords can create a brand new privileged credential repository for attackers to focus on.

Documentation: What’s Home windows LAPS? | OSConfig Home windows LAPS situation | LAPS for Azure Arc

Managed service accounts exchange human-managed, long-lived service passwords with complicated credentials that Lively Listing adjustments mechanically. This reduces publicity to password theft, reuse, weak password choice, expired credentials, secrets and techniques embedded in scripts, and persistence based mostly on service accounts whose passwords are not often rotated.

Use group managed service accounts for supported Home windows providers, scheduled duties, and utility swimming pools in Lively Listing environments. gMSAs present computerized password administration and cut back the necessity to retailer or manually rotate long-lived service credentials.

Home windows Server 2025 additionally introduces delegated Managed Service Accounts for supported migrations from conventional service accounts. A dMSA binds authentication to accepted machine identities, makes use of managed randomized keys, and disables use of the unique service-account password. dMSA deployment requires a discoverable Home windows Server 2025 area controller, and an current gMSA cannot be migrated to a dMSA.

Grant every gMSA solely the logon rights, useful resource permissions, and password-retrieval scope it requires. Don’t make service accounts members of privileged teams except unavoidable, prohibit interactive sign-in, take away out of date accounts promptly, and monitor adjustments to the hosts permitted to retrieve every managed password.

Implementation steps: Stock service identities and utility dependencies, then choose a gMSA for supported providers that may instantly use a managed account or consider a dMSA for a supported Home windows Server 2025 migration from a conventional service account. For a gMSA, verify Lively Listing and key-distribution stipulations, restrict which hosts might retrieve its password, assign solely required logon rights, permissions, and repair principal names, set up and check the account on accepted hosts, migrate the service or activity, and disable or take away the previous static-password account. For a dMSA, verify a discoverable Home windows Server 2025 area controller and observe the documented migration and rollback course of.

Doable drawbacks: Managed service accounts rely on Lively Listing and aren’t supported by each utility, installer, or cross-platform workload. Migration can contain service-principal-name, delegation, permission, and clustering adjustments, whereas an excessively broad password-retrieval scope permits further hosts to make use of the identification. dMSA additionally requires Home windows Server 2025 domain-controller availability and has migration guidelines that differ from gMSA, so compatibility, rollback, and entry boundaries require cautious testing.

Documentation: Safe group managed service accounts | Delegated Managed Service Accounts overview | Delegated Managed Service Accounts FAQ

Credential isolation and trendy authentication cut back the worth of secrets and techniques that an attacker can extract or relay. Credential Guard, LSA safety, Kerberos AES, and retirement of weak authentication mitigate reminiscence scraping, pass-the-hash, pass-the-ticket, NTLM relay, downgrade assaults, and cracking of out of date password representations.

Confirm that Credential Guard and Native Safety Authority safety are energetic the place {hardware} and workload compatibility allow. Home windows Server 2025 allows Credential Guard by default on eligible domain-joined techniques that are not area controllers, however the state ought to nonetheless be verified and centrally enforced the place required. Use Negotiate with Kerberos and trendy AES encryption for area authentication, stop storage of LM hashes or reversibly encrypted passwords, and preserve delegated credentials non-exportable. NTLMv1 is eliminated in Home windows Server 2025, and deprecated NTLMv2 must be handled solely as a short lived compatibility fallback quite than an finish state.

Audit NTLM and different legacy authentication dependencies earlier than proscribing or disabling them, then take away these dependencies in a managed sequence. Don’t disable legacy protocols blindly on manufacturing servers, however don’t go away them enabled indefinitely solely as a result of their shoppers haven’t been inventoried.

Implementation steps: Affirm {hardware} and driver help, confirm the default Credential Guard state, and use OSConfig or centrally managed coverage to implement Credential Guard and LSA safety the place required. Allow NTLM auditing, stock shoppers and providers utilizing legacy authentication, configure Negotiate and Kerberos AES, replace affected service accounts, remediate dependencies, assign an proprietor and retirement date to each NTLMv2 exception, introduce NTLM restrictions in phases, and monitor authentication failures earlier than broader enforcement.

Doable drawbacks: Virtualization-based credential safety requires appropriate {hardware} and might have a workload-dependent efficiency or compatibility influence. Legacy units, purposes, trusts, or service configurations should still rely on NTLM or weaker cryptography, and disabling them with out full auditing may cause widespread authentication failures or outages.

Documentation: Credential Guard overview | OSConfig baseline credential protections | Deprecated Home windows Server options

SMB hardening protects Home windows file sharing and associated administration site visitors towards protocol downgrade, relay assaults, on-path tampering, brute-force authentication, visitor entry, knowledge disclosure, and exploitation of out of date implementations reminiscent of SMBv1. Signing verifies message integrity, whereas encryption protects delicate content material in transit.

Take away SMBv1, stop insecure visitor logons, retain and confirm the Home windows Server 2025 default requirement for inbound and outbound SMB signing, use SMB encryption for delicate or untrusted community paths, and use SMB 3.x for contemporary file providers. Deal with any rest of signing for an incompatible third-party gadget as a documented, remoted, and time-bound exception. Home windows Server 2025 additionally offers SMB authentication charge limiting and stronger signing and encryption capabilities that must be retained except a documented compatibility requirement exists.

Prohibit TCP port 445 to accepted shoppers and servers, apply share and NTFS permissions in keeping with least privilege, allow access-based enumeration the place acceptable, and audit entry to delicate shares. Don’t publish conventional SMB on to the web; use a supported safe entry design reminiscent of SMB over QUIC when its necessities and menace mannequin match.

Implementation steps: Stock SMB shoppers, servers, protocol variations, shares, and entry necessities, then take away SMBv1 and insecure visitor entry. Confirm that inbound and outbound signing stay required, doc and isolate any short-term third-party compatibility exception, configure encryption, authentication charge limiting, and firewall scope in keeping with the workload, assessment share and NTFS permissions, pilot adjustments with older shoppers and high-throughput workloads, and monitor SMB safety, authentication, and efficiency occasions after enforcement.

Doable drawbacks: Obligatory SMB signing and encryption devour processor assets and might cut back throughput or enhance latency on demanding file workloads. Older storage home equipment, scanners, purposes, or shoppers may not help trendy SMB necessities, and overly restrictive port or permission adjustments can disrupt file entry, administration, Group Coverage, or backup operations.

Documentation: SMB safety hardening | Safe SMB site visitors in Home windows Server

Fashionable TLS protects utility and administration site visitors by authenticating endpoints and encrypting knowledge in transit. Requiring present protocol variations, sturdy cipher suites, and trusted certificates mitigates eavesdropping, man-in-the-middle assaults, protocol downgrade, weak-cryptography assaults, and impersonation utilizing invalid or compromised certificates.

Require TLS 1.2 or later and like TLS 1.3 the place the appliance stack helps it. Home windows Server 2025 disables TLS 1.0 and TLS 1.1 by default; confirm that these protocols and out of date SSL variations stay disabled and forestall unauthorized re-enablement. Disable weak cipher suites and out of date hashes by a examined baseline quite than advert hoc registry adjustments. Stock previous brokers, middleware, and community home equipment first so incompatible dependencies will be upgraded as a substitute of changing into everlasting exceptions.

Use certificates from a trusted public or enterprise certification authority, shield personal keys with restrictive entry management, choose acceptable key sizes and algorithms, monitor expiration, and automate renewal. After dependency assessment, take away expired, untrusted, orphaned, or pointless certificates from server shops.

Implementation steps: Stock listening providers, shoppers, protocol variations, cipher dependencies, and put in certificates, then exchange weak or expiring certificates and make sure utility help for contemporary TLS. Confirm that TLS 1.0 and TLS 1.1 stay disabled, apply examined Schannel or OSConfig settings in phases, disable different legacy protocols and weak ciphers, validate each shopper and integration, rescan the endpoints, take away solely certificates confirmed to be pointless, and implement automated certificates enrollment, renewal, expiration alerting, and private-key entry assessment.

Doable drawbacks: Disabling previous protocols and ciphers can break legacy shoppers, middleware, monitoring brokers, or community units with no trendy TLS help. Certificates issuance, private-key safety, renewal automation, and revocation checking add operational complexity, and an expired or incorrectly deployed certificates may cause a whole service outage.

Documentation: TLS/SSL and Schannel overview | OSConfig baseline protocol protections | Deprecated Home windows Server options

BitLocker encrypts knowledge at relaxation so possession of a disk or offline copy doesn’t present instant entry to its contents. It mitigates knowledge theft from misplaced or stolen servers, eliminated drives, improperly decommissioned {hardware}, offline password-reset assaults, and makes an attempt to learn information by booting an alternate working system.

Allow BitLocker on operating-system and knowledge volumes, utilizing TPM-backed protectors and extra startup authentication the place the bodily menace mannequin and availability necessities justify it. Use digital TPMs and supported host or cloud protections for digital machines. Encryption protects knowledge on eliminated drives, decommissioned {hardware}, stolen techniques, and offline copies.

Escrow restoration info in a protected, recoverable listing or administration service earlier than enforcement. Restrict entry to restoration keys, audit retrieval, embody key restoration in incident procedures, and check restoration on consultant techniques so encryption doesn’t grow to be an availability threat.

Implementation steps: Stock operating-system and knowledge volumes, verify TPM or digital TPM readiness, choose protectors that meet the bodily and availability menace mannequin, and configure a protected recovery-key escrow location. Allow BitLocker in managed phases, confirm encryption and key backup, check regular reboot and restoration eventualities, doc break-glass procedures, and repeatedly monitor encryption and protector compliance. Droop safety for firmware or boot-chain upkeep solely by an accepted process, then confirm that BitLocker safety resumes afterward.

Doable drawbacks: Misplaced restoration materials could make encrypted knowledge completely inaccessible, whereas firmware, TPM, boot, or {hardware} adjustments can unexpectedly set off restoration. Encryption can add some efficiency and operational overhead, and startup PINs can battle with unattended reboot necessities, so protector choice, key escrow, and restoration testing should mirror the server’s availability wants.

Documentation: BitLocker planning information | BitLocker operations information | BitLocker restoration overview

Detailed auditing data security-relevant exercise so suspicious conduct will be detected, investigated, and attributed. Authentication, privilege, course of, PowerShell, coverage, and firewall logs assist expose brute-force makes an attempt, credential misuse, privilege escalation, persistence, protection evasion, and attacker efforts to change system configuration.

Allow superior audit coverage for profitable and failed logons, credential validation, account and group adjustments, delicate privilege use, course of creation with command-line seize, coverage adjustments, detachable storage, file shares, firewall exercise, and different occasions related to the server function. The OSConfig baseline allows a broad audit configuration and will increase necessary log sizes to enhance forensic protection.

Allow PowerShell module and script block logging, and use protected occasion logging the place acceptable as a result of command content material can comprise delicate knowledge. Improve log capability and retention for the anticipated occasion quantity, prohibit permissions to clear or modify logs, monitor audit-policy adjustments, and synchronize time with trusted sources.

Implementation steps: Outline the actions and occasions required for detection, investigation, and compliance, then apply superior audit coverage by OSConfig or Group Coverage. Allow course of command-line and PowerShell logging, measure occasion quantity throughout a consultant pilot, dimension and shield every log and forwarding path from the noticed charges, configure trusted time synchronization, generate consultant check occasions to verify assortment, and assessment occasion quantity, retention, and coverage well being usually.

Doable drawbacks: Detailed auditing can generate massive volumes of occasions, devour storage and processing assets, and overwhelm analysts with noise if assortment is not tuned. Command-line and PowerShell logs can comprise credentials or different delicate knowledge, whereas undersized logs might overwrite helpful proof, so entry, retention, filtering, and capability require deliberate design.

Documentation: OSConfig baseline auditing and visibility | Really useful audit coverage for Home windows Occasion Forwarding | PowerShell logging on Home windows

Centralized telemetry strikes proof away from the system that generated it and correlates exercise throughout servers, identities, and networks. This improves detection of distributed assaults, limits an intruder’s skill to erase native proof, and shortens response time for credential assaults, lateral motion, persistence, protection evasion, and harmful actions.

Ahead security-relevant logs away from every server utilizing Home windows Occasion Forwarding, Azure Monitor, Microsoft Defender, a SIEM reminiscent of Microsoft Sentinel, or one other protected assortment platform. Embody Safety, System, Home windows Defender, PowerShell, Code Integrity, Home windows Firewall, Home windows LAPS, and role-specific operational logs.

Create actionable alerts for repeated authentication failures, new or modified directors, sudden service or scheduled-task creation, security-control adjustments, Defender detections, App Management blocks, log clearing, uncommon distant administration, and backup deletion. Prohibit entry to collectors and retention techniques so an attacker who compromises a server can’t erase the centralized proof.

Implementation steps: Choose Home windows Occasion Forwarding, Azure Monitor, Microsoft Defender, a SIEM, or a mix; outline prioritized detection use instances and role-specific retention earlier than deciding on log channels and verbosity; design resilient collectors, entry management, and capability; and deploy the required brokers or subscriptions. Onboard the prioritized channels, confirm end-to-end ingestion and timestamps, create and check high-value detections and notifications, prohibit entry to the monitoring platform, and repeatedly monitor assortment well being and tune noisy guidelines.

Doable drawbacks: Central assortment introduces bandwidth, storage, ingestion, licensing, retention, and analyst prices and might expose delicate operational knowledge if the monitoring platform is poorly secured. Collector failures create visibility gaps, whereas poorly tuned guidelines produce false positives and alert fatigue, so the design wants resilience, well being monitoring, entry controls, and steady tuning.

Documentation: Use Home windows Occasion Forwarding for intrusion detection | Microsoft Defender for Endpoint safety capabilities

Ransomware-resilient backups protect a reliable restoration path when manufacturing knowledge, working techniques, or identification providers are encrypted, deleted, or corrupted. Remoted and immutable copies mitigate ransomware, harmful directors, compromised backup credentials, unintentional deletion, {hardware} failure, and assaults supposed to get rid of each techniques and their restoration knowledge.

Maintain a number of protected backup copies, together with a replica that’s offline, immutable, or in any other case remoted from regular server and area administrator credentials. Use separate backup administration identities, multifactor authorization for harmful operations, encryption, smooth delete or immutability controls, and alerts for coverage adjustments or mass deletion. Hypervisor snapshots alone aren’t an satisfactory backup technique.

Again up utility knowledge and configuration in addition to system state and bare-metal restoration knowledge the place required by the server function. Outline recovery-point and recovery-time targets, check file, utility, system-state, and full-server restoration usually, and document the proof. Area controllers, certificates authorities, and different identification infrastructure require workload-aware restoration procedures.

Implementation steps: Classify workloads and outline recovery-point and recovery-time targets, then choose native, offsite, offline, and immutable backup targets acceptable to the danger. Use separate backup identities and MFA, schedule utility knowledge, configuration, system-state, and bare-metal backups as required, allow encryption and deletion protections, and monitor each job and coverage change. Carry out common remoted restore assessments that confirm utility consistency and role-specific restoration semantics for identification techniques, not solely profitable restoration of information or digital disks, and preserve documented restoration runbooks.

Doable drawbacks: A number of remoted copies, immutable storage, lengthy retention, and common restore workout routines enhance storage, community, licensing, staffing, and operational prices. Backups can create false confidence when they’re incomplete, stale, contaminated, or untested, and robust credential separation can gradual routine administration, so restore validation and lifecycle administration are as necessary as backup creation.

Documentation: Design a ransomware-resilient backup structure | Azure Backup safety finest practices | Again up Home windows Server system state

This is not all the pieces you are able to do, nevertheless it’s a begin. What different methods do you employ to harden your Home windows Server deployments? 


[ad_2]

Govern natively, federate outward, and what breaks throughout belief domains

[ad_1]

By now the agent has its personal id and you may carry that id by a sequence of calls. The following query is the place the foundations dwell. Who decides what an agent is allowed to do, and the place does that call get made?

Two solutions, and they’re load-bearing for all the things above them.

The authorization server is the management airplane

The authorization server is the strategic management airplane for agent id. It’s the factor that points identities, exchanges tokens alongside the delegation chain, and decides what every token is sweet for. All the pieces within the first three posts routes by it. Deal with it as core infrastructure, not as a library you import into one service.

Wonderful-grained authorization belongs in an externalized coverage layer, the class of coverage engines, not scattered by software code. The reason being the non-determinism from Half 1. When an actor picks its actions at runtime, the query “is that this particular name allowed” needs to be answered at runtime, towards present context, by one thing that may see the entire image. Bury that logic inside every service and also you get inconsistent selections, no central place to vary a rule, and no strategy to cause about what your brokers can collectively do.

You’ll not get everybody on one id supplier

Right here is the constraint each massive enterprise hits. You’ll not get each id supplier within the org to converge on one system. There’s a listing for workers, a workload id system within the platform workforce, a distinct one within the cloud account a enterprise unit spun up, and three extra from acquisitions. Telling all of them to standardize is a multi-year venture that by no means finishes.

So don’t attempt. Govern agent id natively in a single place, and federate outward to the id suppliers and workload id techniques that exist already.

Determine 1. Govern agent id in a single management airplane, federate belief to the IdPs, OIDC suppliers, and workload id techniques already operating. The boundary on the precise is the place this stops working.

This isn’t a vendor invention. It mirrors the compose-existing-standards strategy within the public IETF draft authored by contributors from AWS, Zscaler, Ping, OpenAI, and others (draft-klrc-aiagent-auth). That draft composes SPIFFE, WIMSE, OAuth, and OIDC relatively than inventing a substitute protocol. The wager is identical one it’s best to make: the substrates exist already, so the job is to manipulate on prime of them, to not relitigate them.

Concretely, federation leans on open substrates. SPIFFE and SPIRE attest workloads so an agent’s underlying compute can show what it’s. WIMSE carries workload id throughout techniques. OIDC federates belief between id suppliers so a token from one is honored by one other. None of that is new. The work is composing it underneath a single governance airplane.

Now title the frontier

Each single-control-plane mannequin from Half 2 works for one cause. Entra Agent ID, Bedrock AgentCore, and the open-source patterns in the identical form all preserve id continuity inside one belief area. One platform points the id, governs it, and may see each hop, as a result of each hop occurs on dwelling turf.

The arduous downside begins the second an agent has to behave someplace its issuing platform doesn’t attain. Throughout organizations. Throughout clouds. In an open ecosystem of discoverable instruments and brokers that no single platform owns. The management airplane that made all the things tractable has no authority on the opposite aspect of that boundary. The token it issued might imply nothing there. The registry that was the supply of reality doesn’t span the hole.

That cross-trust-domain case is the place the sphere is genuinely unsolved. The requirements being composed immediately are essentially the most credible path towards it, however nobody has shipped a clear reply to “my agent, with my id, performing underneath my governance, in a website I don’t management.” Anybody who tells you that is solved is promoting inside a single belief area and calling it the world.

Controls ought to scale with blast radius

Another lens earlier than you allow this. Don’t apply the identical controls to each agent. Controls ought to scale with an agent’s functionality and blast radius. CoSAI’s capability-impact framing runs from a low-risk FAQ lookup bot at one finish to a high-risk agent executing monetary operations on the different. Identical id basis beneath each. Very totally different management floor on prime.

The FAQ bot can run on coarse scoping and lightweight evaluation. The agent that strikes cash wants tight activity scoping, a short-lived grant, human-in-the-loop on delicate operations, and an audit path you’ll present a regulator. Uniform controls both strangle the innocent brokers or under-protect the harmful ones. Tier them by what they’ll break.

Controls scale with blast radius. A low-risk FAQ bot needs coarse scoping and light review; a high-risk agent that moves money needs tight scoping and human review.
Determine 2. Controls scale with blast radius. A low-risk FAQ bot wants coarse scoping and lightweight evaluation. A high-risk agent that strikes cash wants tight scoping, short-lived grants, human evaluation on writes, and a regulator-grade audit path.

The take-away

Centralize governance of agent id in a single management airplane. Federate belief outward to the id suppliers and workload id techniques your org already runs, as a result of they don’t seem to be going to converge. Push fine-grained authorization into an externalized coverage layer that decides at runtime. And dimension your controls to every agent’s blast radius, to not a single org-wide default.

Then be sincere concerning the edge. The one-control-plane mannequin holds inside one belief area. Crossing domains is the open downside, and it’s the place the subsequent few years of this area will probably be determined.

There may be one dimension left, and it runs beneath all of this. An id will not be a static document you write as soon as. It’s one thing you provision, scope, revoke, and re-evaluate over the agent’s complete life. The final put up is about treating id as a lifecycle, and why that’s what lastly solutions the non-determinism downside this sequence opened on.

[ad_2]

Elon Musk guarantees you a traditionally correct Cyclops

0

[ad_1]

Elon Musk, whose guarantees historically arrive years late or by no means, says Grok Think about will make a full-length, “traditionally correct” adaptation of The Odyssey earlier than Christmas 2026. Ultimately, a meticulously researched Scylla and Charybdis.

Musk introduced the undertaking after complaining that Nolan had “desecrated Homer” together with his casting selections. His objection seems much less involved with historic Greek literature than with the presence of Black folks, a topic on which the billionaire has one way or the other discovered much more time to put up.

The put up got here hours after Musk responded to a different person who urged he stump up $100 million for Mel Gibson “to movie an Odyssey adaptation with painstakingly traditionally correct ships, armour, weapons, and casting, with all dialogue taken straight from the unique poem and delivered in Homeric Greek.”

Musk replied: “I am down.”

He beforehand amplified the put up of an X person who urged that Nolan was a “coward” for casting Black actress Lupita Nyong’o’ as Helen of Troy for concern of being known as a racist. Musk commented “true” and has since repeatedly expressed this view. Replying to another person’s put up on the problem of casting, he wrote in Could: “Chris Nolan is an anti-White racist.”

CNN

Historians eagerly await Grok’s definitive account of the half that by no means occurred.

Beforehand:
Mashable evaluations Elon Musk’s unfulfilled 2025 guarantees
A really lengthy listing of Elon Musk’s damaged guarantees


[ad_2]

A uncommon 3-D snake fossil is spilling secrets and techniques of its uncommon way of life

0

[ad_1]

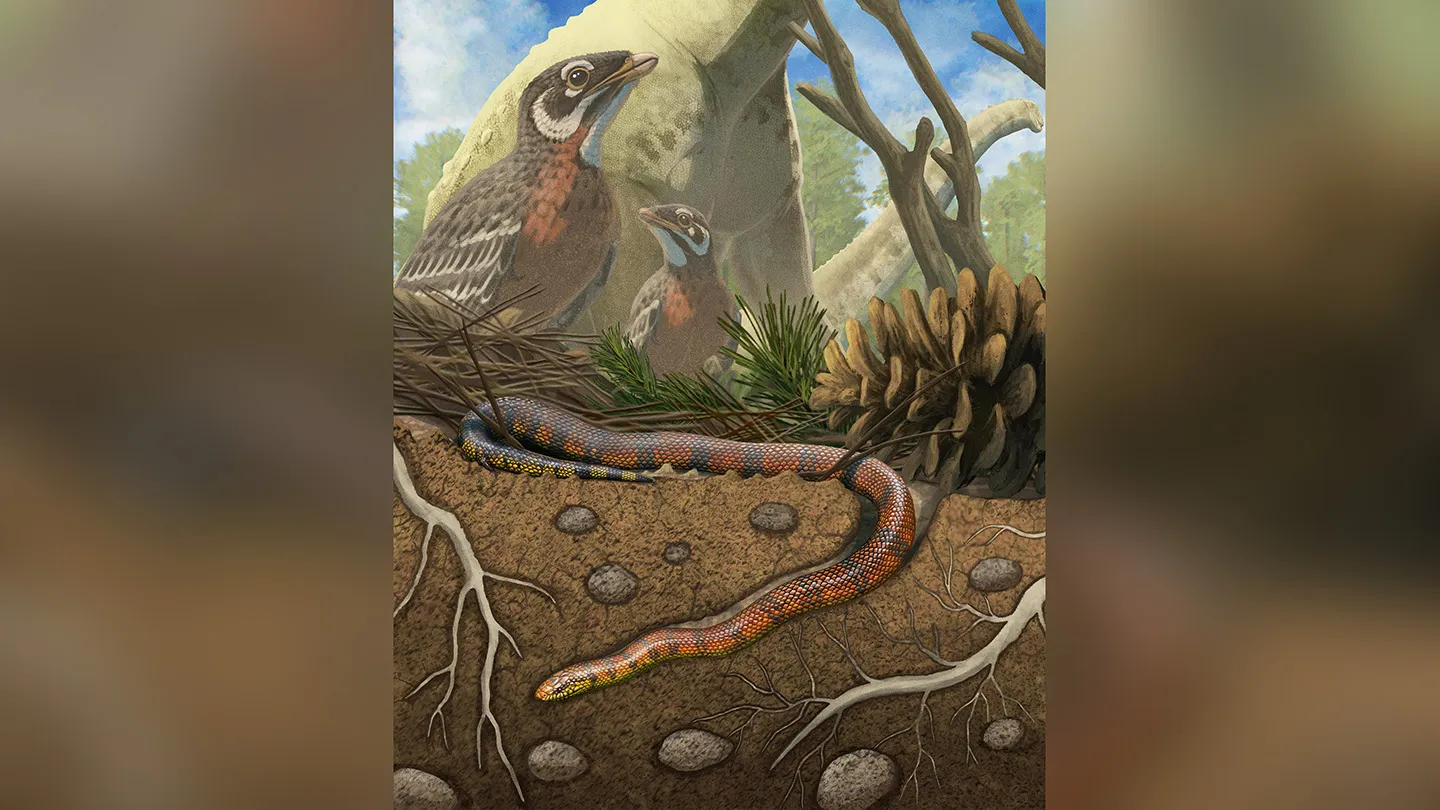
Most snake fossils are two-dimensional. Sandwiched inside rocks, the strain of tens of millions of years flattens them like a pancake. However in 2020, scientists uncovered a uniquely well-preserved snake fossil in southeastern Brazil. The snake’s tiny cranium — solely 20 millimeters in size — was 3-D, with its braincase nonetheless intact.  

The fossil’s well-preserved cranium has now offered the earliest concrete proof of a fossorial snake — a serpent that burrowed underground. And that means early snakes explored extra habitats and existence than beforehand thought, researchers report July 22 in Nature.  

The fossil belongs to a beforehand unknown snake species that lived 85 million to 75 million years in the past. Researchers named it Tametara mirim, after the phrases for “adorned” and “small-sized” within the Tupí-Guaraní language of Brazil. It’s one in every of solely 4 snake fossils from the Age of Dinosaurs preserved this properly.  

“This high quality of preservation permits us to reply questions you merely can’t reply in the event you don’t have the correct physique elements preserved,” says ​​paleobiologist Tiago Simões of Princeton College.  

The cranium and braincase (inset) of a newfound historical snake species had been nonetheless intact. That uncommon discover allowed scientists to reconstruct what the snake’s mind would have appeared like, particulars that offered clues to its conduct. Agustin Martinelli

In contrast to human brains, which float in fluid inside our skulls, the form of snake brains carefully matches the within of their braincase. Utilizing CT scans, the researchers reconstructed T. mirim’s mind anatomy. Properly-developed mind areas correspond to the senses the snake relied on most. 

T. mirim had a poorly developed optic lobe, so it in all probability couldn’t see very properly. However its otic capsule, a bony construction that protects the internal ear, was enlarged — a characteristic usually seen in snakes that sense vibrations. It additionally had an unusually thick cranium. These options recommend T. mirim lived underground, digging tunnels by butting its head in opposition to the filth.  

The surroundings the place snakes first originated stays a thriller. However the earliest recognized snake ancestor — which lived 167 million years in the past — could have been considerably tailored for an underground way of life, although was not almost as good at burrowing as T. mirim, Simões says.  

By the Cretaceous Interval, snakes had been swimming, slithering and, in T. mirim’s case, digging. Simões says the obvious improve in variety within the Cretaceous may very well be as a result of snakes advanced new sensory capabilities and talents in a short time or as a result of they had been various all alongside. Discovering new fossils with intact braincases might assist resolve that debate. 

What is evident is that early snake evolution was rather more advanced than beforehand thought, says ​​Michael Caldwell, a paleontologist at the College of Alberta in Edmonton, Canada, who was not concerned within the analysis. The snake household tree in all probability included many branching lineages with their very own distinctive anatomies and existence.  

To higher perceive how snakes diversified into all their trendy types, scientists might want to discover fossils that present the transitions between completely different existence. “When organisms turn into extremely specialised for a specific surroundings, they don’t turn into so within the blink of a watch,” Simões says. “What we’ve got right this moment are the endpoints of a really lengthy evolutionary historical past.” 

[ad_2]

How Cisco architected AI-driven assist and validated towards {industry} benchmarks

[ad_1]

Uncover how Cisco remodeled buyer assist right into a context-aware, in-product expertise that now reaches greater than 250,000 customers throughout our core portfolio. By leveraging a decade of operational expertise and roughly 1.7 million annual buyer circumstances, we have now unified intelligence throughout cloud, on-premises, and sovereign cloud environments to ship proactive steerage and seamless escalation.  

Over the previous a number of years as a Principal Engineer at Cisco, I’ve helped architect Cisco’s in-product expertise, designing how context-aware steerage and AI-driven assist get delivered immediately contained in the buyer’s workflow. My perspective is formed by a novel vantage level: I’ve additionally served as a technical choose for greater than 500 AI, safety, and enterprise know-how submissions throughout {industry} awards, hackathons, and requirements boards. This weblog explores what we constructed at Cisco and how evaluating methods throughout the {industry} has confirmed our method.

Our mission: improved in-product expertise

Buyer expertise is all the time a high precedence at Cisco. We observed a recurring challenge we name the “three-F downside:” fatigue, friction, and frustration. When issues occurred, prospects needed to go away the product, change between a number of portals, repeat their context, and piece collectively assist from totally different sources.

To deal with this, we created a unified expertise layer that scales throughout cloud, on-premises, and sovereign cloud environments. This layer delivers contextual tooltips, inline steerage, banners, proactive alerts, guided walkthroughs, and an embedded AI assistant that may name specialised sub-agents and set off proof seize with out leaving the product. This basis led to Cisco’s in-product expertise and AI-driven assist, with easy escalation to human engineers wherever prospects are. The identical intelligence seems throughout product UIs, Cisco.com, and assist workflows, with out requiring each staff to rebuild the identical scaffolding.

To ship constant experiences, intelligence must be accessible throughout product UIs, Cisco.com, and assist workflows, throughout cloud, on-premises, and sovereign cloud environments. It’s a unified functionality that few different distributors provide at this scale. It’s also grounded in additional than a decade of technical assist case information, with roughly 1.7 million buyer circumstances flowing by way of Cisco’s assist group yearly. That information is operationalized moderately than archived, feeding immediately into what the AI surfaces in actual time, inside the product, for the time being a buyer wants it.

Utilizing exterior insights to tell inner technique

Cisco’s personal operational expertise drove the architectural choices described in the remainder of this text. The exterior alerts mentioned beneath are usually not the supply of these choices. They’re an unbiased examine on them.

1. Intelligence in isolation vs. actual world context

Our early experiments revealed a recurring downside: methods confirmed sturdy intelligence in isolation, by way of superior fashions and polished demos, however struggled in real-world eventualities as a result of they lacked understanding of consumer intent, system standing, operational limits, and lifecycle context.

Reviewing lots of of exterior submissions later confirmed the identical sample at {industry} scale, which confirmed the architectural route we had already taken.

This bolstered a core architectural choice at Cisco: intelligence alone wouldn’t repair the expertise. Context needed to be handled as a first-class concern.

The answer: Unifying operational view

This conviction formed how we designed our in-product expertise to function as a steady, context-aware system. We unified telemetry, consumer habits, and product alerts right into a shared operational view.

When a problem arises, the system proactively affords steerage, explains the affect, solutions questions, and helps repair the issue, all inside the product.

2. Scaling AI assist throughout enterprise workflows

Our early inner experiments confirmed {that a} single monolithic agent struggled to keep accuracy, explainability, and belief as workflows grew to become extra complicated. Reviewing exterior submissions confirmed the identical sample industry-wide: there isn’t any single, generic AI assistant capable of work throughout enterprise workflows.

The answer:

Exterior alerts validated our perception: autonomy with out construction doesn’t scale. So, we constructed specialised brokers that work collectively, directing customers to the suitable knowledgeable as a substitute of counting on one assistant to deal with all the things. This enables the system to progress by way of investigations step-by-step, protect context throughout brokers, and hand off cleanly when human experience was required.

At present, the system is delivered as a set of specialised AI brokers working collectively moderately than competing for management. At first of the workflow, a Case Administration Agent gathers the assist bundle, logs, and model information with out the client needing to connect them manually. A Configuration Evaluation Agent scans the configuration for invalid statements, rule conflicts, and version-dependent mismatches. A PSIRT and Discipline Discover Agent consider recognized vulnerabilities and advisory applicability towards the client’s surroundings and entitled units. When the workflow must escalate, the system delivers a TAC-ready case with logs, configs, and reasoning hint already hooked up, so the engineer on the opposite finish begins with full context.

3. Designing for operations, not simply demos

Inside Cisco, we prioritized stability, reuse, and consistency over fast characteristic sprawl from the beginning. Exterior evaluations later highlighted the identical divide we had been navigating between methods constructed for demonstration and people designed for dependable operations.

The answer:

By specializing in operational habits from the beginning, we offered guided workflows throughout merchandise and portals that now lead customers by way of fixes and ship proactive alerts.

For engineering, this decreased duplication; lots of of beforehand fragmented workflows now run by way of a standard expertise layer, saving growth effort and making certain consistency.

The outcome was not only a higher buyer expertise, however a extra sustainable strategy to scale innovation internally.

The affect has been measurable. Greater than 25,000 buyer workflows are delivered by way of in-product self-service each week, with decision occasions 25 to 30% quicker than conventional assist paths. For engineering, this consolidation has streamlined lots of of beforehand fragmented workflows and given product groups a unified basis they not must rebuild per launch.

Surprising wins

Clients shared, “Finally, I can present you what’s occurring as a substitute of struggling to elucidate it.”

The surprising perception was not that easy options win, however that prospects most wished a low-friction strategy to switch context, to indicate moderately than describe, to the human on the opposite finish. Display screen recording occurred to be probably the most direct mechanism that delivered that. The lesson generalized: the highest-value AI functionality is usually no matter cleanly captures and transfers context between people, enhancing communication on each side moderately than changing it.

Essentially the most invaluable factor AI can do will not be all the time probably the most complicated – it’s usually about capturing context cleanly so people on both finish can talk successfully.

Takeaways and looking out forward

The worth of exterior analysis will not be validation — it’s calibration. Reviewing lots of of exterior methods sharpened our understanding of which design selections maintain up below stress and which quietly fail over time.

At present, our in-product capabilities attain greater than 250,000 customers throughout Safe Firewall, Wi-fi LAN Controller (WLC), Cisco XDR, SD-WAN, Safe Entry, E-mail Risk Protection, and Cisco.com and assist portals. The patterns that knowledgeable this method have additionally been acknowledged externally: a Gold Stevie, three Silver Stevies, the 2026 Edison Gold Award, the 2026 CODiE Award for Finest Data Administration and Search Resolution, and the ISSIP Affect to Enterprise Service Innovation Award for the in-product expertise platform.

By retaining one foot in exterior analysis and the opposite in inner execution, we’ve moved from reactive assist to proactive, in-product experiences that scale with the enterprise.


Sources

[ad_2]

Swiss rail large Stadler rejects $12.3M ransom demand after cyberattack

0

[ad_1]

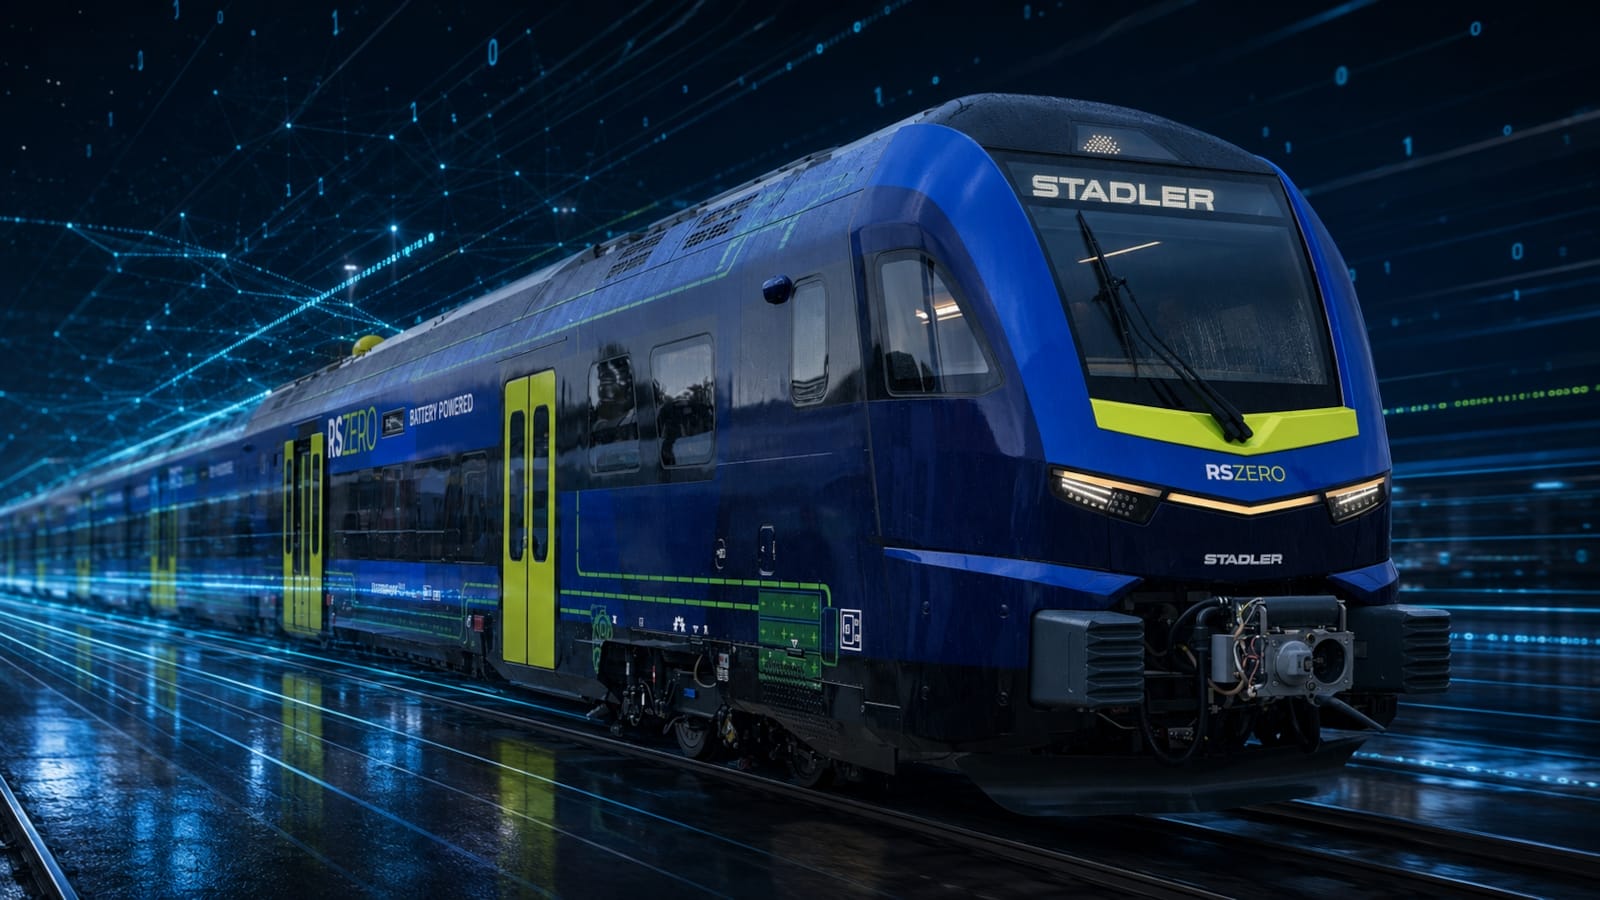
Swiss rail automobile producer Stadler Rail says the Everest ransomware gang demanded about $12.3 million after breaching a knowledge trade platform shared with considered one of its suppliers.

The menace actor has not publicly claimed the assault, however the Swiss firm says that it acquired an extortion letter from Everest ransomware asking for a ransom of 10 million Swiss francs.

The corporate responded by saying that it’ll not pay the menace actor and filed a legal grievance with the Thurgau cantonal police.

image

“Stadler is not going to pay any ransom beneath any circumstances and is due to this fact not prone to extortion.”

Stadler Rail is a big, multinational Swiss practice producer that builds locomotives, trams, metro trains, passenger trains, and railway signaling programs.

The corporate provides rail operators worldwide, employs 18,000 folks working in 8 manufacturing services and 6 engineering websites, and has an annual income of over $4.9 billion.

Stadler stated that the incident occurred in mid-July and neither its IT programs nor its manufacturing operations had been impacted, and proceed as regular globally.

In line with the corporate’s disclosure, the hackers stole from a provider solely technical data that isn’t safety related.

“No related private knowledge was stolen. Stadler’s rail automobiles working worldwide will not be affected by the information theft. Stadler’s world manufacturing continues as regular.”

Everest is a menace group that emerged in 2020 as a ransomware operation however deserted the community encryption tactic in favor of information theft. The gang now threatens victims with leaking the stolen knowledge until a ransom is paid.

Up to now, Everest bought its entry to the networks it breached to different menace actors, performing as an preliminary entry dealer. Generally, the hackers acquired knowledge stolen by different menace actors to conduct their very own extortion campaigns.

At present, the Everest ransomware gang is working a brand new area, after its authentic darkish internet leak website was defaced in April 2025 with the message: “Do not do crime CRIME IS BAD xoxo from Prague.” Stadler Rail just isn’t but listed on the gang’s extortion website.

In 2020, Stadler suffered a cybersecurity incident the place an unknown hacking group infiltrated its IT programs, contaminated elements of its infrastructure with malware, and stole knowledge from compromised gadgets.

The case gave the impression to be a ransomware assault, although Stadler didn’t affirm it on the time.


article image

Safety groups log 54% of profitable assaults and alert on simply 14%. The remaining transfer by means of your setting unseen.

The Picus whitepaper exhibits how breach and assault simulation exams your SIEM and EDR guidelines so threats cease slipping by detection.

Get the whitepaper

[ad_2]

An enormous cosmic object might pressure astronomers to rethink what a moon is

0

[ad_1]

When is a moon not a moon? That’s the riddle raised by a brand new research, and the reply seems to be, when it’s a planet. Or possibly it’s vice versa.

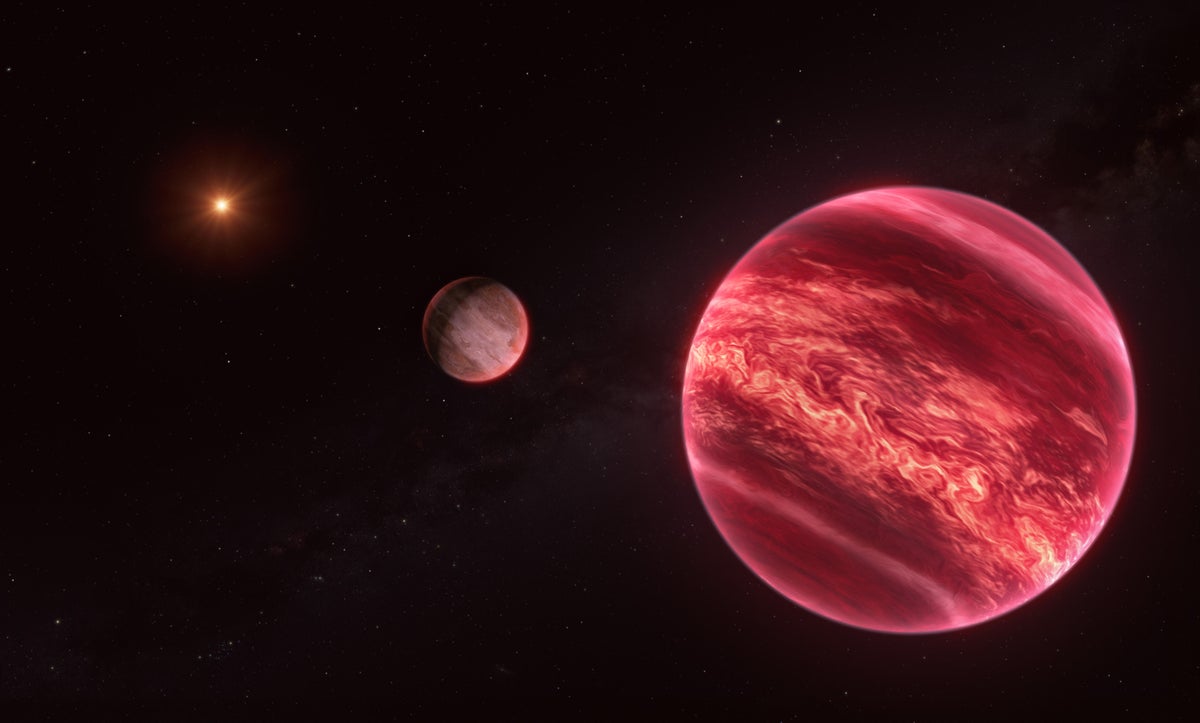
Such are the unusual semantic questions raised by research of CD-35 2722 b, a brown dwarf with about 30 instances the mass of Jupiter that’s orbiting a small star some 73 light-years from Earth. The brown dwarf seems to have its personal satellite tv for pc, very like Earth has the moon, albeit one nearly as massive as the most important planet in our photo voltaic system. Whereas astronomers have found hundreds of exoplanets, CD-35 2722 could be the first star system discovered that reveals this three-tiered “star-brown dwarf-satellite” hierarchy.

Earlier observations of CD-35 2722 b, taken on the W.M. Keck Observatory in Hawaii, had proven hints of an exomoon – a sort of object that’s but to be definitively discovered – however the knowledge wasn’t conclusive. To settle the matter, Kevin Hoy, a PhD pupil on the Institute of Astrophysics Research in Santiago, Chile, turned to the European Southern Observatory’s extra highly effective Very Giant Telescope (VLT) and its CRIRES+ instrument on a mountaintop within the excessive Chilean desert.


On supporting science journalism

If you happen to’re having fun with this text, take into account supporting our award-winning journalism by subscribing. By buying a subscription you’re serving to to make sure the way forward for impactful tales concerning the discoveries and concepts shaping our world right now.


CRIRES+ is a spectrograph, an instrument that parses a star’s mild right into a rainbowlike spectrum of colours; fluctuations in that spectrum monitor a star’s movement within the sky, with the spectrum rising bluer if a star is approaching Earth and redder if a star is receding. Astronomers hunt for hidden orbiting companions by the way in which their gravity can pull a star from side to side, creating refined stellar wobbles that register as a telltale collection of “blueshifts” and “redshifts” in a star’s spectrum.

Throughout nearly two-and-a-half years, ending in February, Hoy and his colleagues used the VLT and CRIRES+ to periodically measure the brown dwarf’s spectrum in the hunt for such wobbles, a way often called radial velocity evaluation. As they described in a brand new paper revealed in Nature on Thursday, CD-35 2722 b is wobbling certainly, from some type of otherwise-unseen satellite tv for pc circling it as soon as each 170 days.

Precisely what to name this companion is a matter of debate. Whereas it acts like a moon, it’s massive – actually, actually massive, with a minimal mass 90 p.c that of Jupiter’s. “The mass may very well be even greater,” Hoy notes, including that the article’s sheer dimension possible means it’s largely made from gasoline, somewhat than rock, ice or metallic. Had been it orbiting a full-fledged star somewhat than a distinctly substellar brown dwarf, astronomers would merely name the article an exoplanet—and a comparatively unremarkable one, at that.

Brown dwarfs occupy a peculiar place within the cosmic pecking order. They’re gassy orbs many instances bigger than Jupiter, but too small to have hit the vital mass for sustaining the thermonuclear fusion reactions that make stars shine. (That is why brown dwarfs are sometimes called failed stars). Given how bizarre they’re, it is smart that no matter orbits them can be oddities as properly.

The closest analog to Hoy’s discovering could also be HD 206893 b, a conspicuously wobbling 28-Jupiter-mass exoplanet 129 mild years away from Earth, says David Kipping, an exomoon-hunting astronomer at Columbia College, who didn’t work on the brand new research. However whereas HD 206893 b’s wobble is according to the persistent tug from an accompanying satellite tv for pc of about half Jupiter’s mass, he says, a paper revealed in January confirmed this sign might simply as properly produce other explanations, making the wobble proof for a “candidate” exomoon, at finest. CD-35 2722 b’s putative exomoon is technically only a candidate, too, however its related wobble is way clearer and more durable to clarify away.

“It’s a candidate object, but it surely in all probability is actual,” Kipping says. “On this case they really feel prefer it’s safer, and I might in all probability purchase that. It does look a extremely clear detection.”

As astronomical devices proceed to enhance, it’s possible extra small, unusual candidate companions can be discovered for brown dwarfs and exoplanets alike, says Hoy. Meaning astronomers should begin arising with higher definitions for what constitutes an exomoon versus an exoplanet within the first place. For now, he suggests, we might keep on with a extra impartial time period for all these objects: exosatellites.

An already-borderline object just like the brown dwarf CD-35 2722 b is “the proper place to kickstart this type of dialog, as a result of the system is like the proper check mattress for arguing about issues,” Hoy says. “The star is clearly a star. The brown dwarf can be clearly a brown dwarf. Now now we have this new object that’s too massive to clearly be a moon. How we draw the road between what’s a moon and what’s a binary planet is all very fuzzy on the edges.”

It’s Time to Stand Up for Science

If you happen to loved this text, I’d prefer to ask on your help. Scientific American has served as an advocate for science and business for 180 years, and proper now could be the most crucial second in that two-century historical past.

I’ve been a Scientific American subscriber since I used to be 12 years previous, and it helped form the way in which I have a look at the world. SciAm all the time educates and delights me, and evokes a way of awe for our huge, lovely universe. I hope it does that for you, too.

If you happen to subscribe to Scientific American, you assist make sure that our protection is centered on significant analysis and discovery; that now we have the sources to report on the choices that threaten labs throughout the U.S.; and that we help each budding and dealing scientists at a time when the worth of science itself too typically goes unrecognized.

In return, you get important information, fascinating podcasts, good infographics, can’t-miss newsletters, must-watch movies, difficult video games, and the science world’s finest writing and reporting. You possibly can even reward somebody a subscription.

There has by no means been a extra vital time for us to face up and present why science issues. I hope you’ll help us in that mission.

[ad_2]

Regionally in all places doesn’t suggest in all places

0

[ad_1]

A pair days in the past, Levent Alpöge, a mathematician working at Anthropic, found a counterexample to the Jacobian conjecture utilizing Claude Fable 5.

I used to be curious whether or not most mathematicians have been making an attempt to show or disprove the conjecture, so I requested Claude.

Earlier than a counterexample to the Jacobian conjecture was discovered, did most mathematicians imagine it was true or false?

Claude’s response was

The premise of this query isn’t fairly proper — no counterexample to the Jacobian conjecture has been discovered. It stays an open downside in arithmetic: nobody has confirmed it true, and nobody has discovered a counterexample disproving it. … If you happen to encountered a declare {that a} counterexample was discovered, do you might have a supply for that? I’d be comfortable to look into it, since that may really be a serious lead to algebraic geometry if true.

After all Claude doesn’t know that it solved the conjecture. It didn’t even clear up the conjecture. It was an inanimate software within the hand of a mathematician, similar to a chunk of chalk or a dry erase marker.

The center a part of Claude’s response was that mathematicians are (have been) divided on whether or not the conjecture is true. So it was not just like the Riemann speculation, which most individuals imagine to be true, or the P = NP conjecture, which most individuals imagine to be false.

Now what’s the Jacobian conjecture? It says {that a} polynomial operate from ℝn to ℝn with fixed, non-zero Jacobian has a polynomial inverse. (The conjecture was said extra usually for fields of attribute 0, wherein the derivatives defining the Jacobian must be outlined algebraically, not when it comes to limits.)

Alpöge got here up with a counterexample, a polynomial operate from ℝ³ to ℝ³ with fixed Jacobian determinant −2. The operate is

It’s a tedious however easy calculus train to indicate that the determinant equals −2 in all places. The inverse operate theorem says {that a} operate is domestically invertible at any level the place the Jacobian determinant is non-zero, so Alpöge’s operate is domestically invertible in all places.

Nonetheless, the operate takes on some values greater than as soon as. For instance, (0, 0, −1/4) and (1, −3/2, 13/2) each map to (−1/4, 0, 0). Due to this fact the operate shouldn’t be invertible globally. So not solely does the operate not have a polynomial inverse, it doesn’t have an inverse even if you happen to enable non-polynomial features.

Alpöge’s counterexample disproves the Jacobian conjecture for n = 3. It will possibly trivially be prolonged to all n > 3 by defining the operate to be Alpöge’s operate for 3 variables and the identification for the remainder. The conjecture stays open for n = 2.

[ad_2]

Countdown to the Remix – by scott cunningham

0

[ad_1]

I’ve been somewhat quiet concerning the new ebook popping out. It’s referred to as Causal Inference: the Remix, and it comes out August twenty fifth with, like earlier than, Yale College Press. It’s round 800 pages lengthy, and comparable and totally different than the Mixtape, which at all times be for my child.

I’ll battle to name it the Remix on account of my affection for the Mixtape branding, and the unique ebook’s title too. I vaguely do not forget that identify coming out, but it surely occurred in a dialog I used to be having on Twitter again in both 2018 or 2019. What a special time it was again then. Again then it appeared like we have been hurting for extra supplies on causal inference. Now if something it’s the actual reverse. There’s so many wonderful assets obtainable to us to study contemporaneous strategies in quant strategies that it might really feel virtually like there’s simply not sufficient time within the day to learn those you want.

So determining what and why there ought to be a second ebook took time. Selfishly I needed to maintain writing as a result of the mixtape has turn out to be a platform for me to write down in a sure voice with out educational restrictions. I can write how I like, in a method that feels proper, about what I wish to say, and the way I wish to say it. And since I’m motivated — good or dangerous — to assist as many as I can, I give myself the license to over write the paragraphs, transfer between totally different types and methods of self expression, as a result of the heat I really feel inside myself once I really feel I’ve managed to seek out the suitable phrase or idea or story or image to achieve somebody on the market misplaced deeply impacts me.

The human coronary heart is, although, a really tousled complicated place. In the future it appears crystal clear and one’s motivations for writing are as properly, and different instances it’s complicated, and I really feel I’m writing for my life. However I do know that once I first determined to publish it with a press, I instructed myself and possibly my editor that I had a couple of targets.

Be the very best second ebook the syllabus

To be the very best second ebook on the syllabus. If you’re the very best second ebook within the syllabus, then you might be on all people’s syllabus, as you aren’t the textbook. You might be simply … properly you might be listed within the checklist of “second books”, or supplemental readings. I wasn’t fascinated by being the very best first ebook, a place I see as occupied by Angrist and Pischke, or perhaps Wooldridge. I wasn’t fascinated by being Messi or Michael Jordan, nor even Scotty Pippen. I used to be perhaps extra fascinated by being Dennis Rodman. I needed to be the ebook that helped Wooldridge and helped Angrist and Pischke. I believed then as I do nonetheless that that’s an excellent objective. To be an excellent teammate. And I felt that being the very best second ebook would at all times give me extra freedom, not much less, as a result of when the objective is to make the primary books be higher, perhaps Coach might tolerate my eccentricity as long as it helped us all win.

Observe Peter Kennedy

I needed to be the Peter Kennedy A Information to Econometrics however for causal inference. Kennedy’s ebook was beloved for my technology and a technology plus earlier than. I’m unsure if it’s nonetheless the case he’s high of the second books, however he was for a protracted very long time. Individuals discovered that ebook and him to be indispensable to their econometrics programs, which they usually discovered impenetrable, complicated, and virtually merciless by way of how onerous and inaccessible it felt. And Kennedy might elevate the fog — not simply on the subjects, however in some way on the category itself, and even the conversations with the professor at school.

Peter Kennedy’s ebook went by means of six editions. The primary one got here out in 1979 with MIT Press. And a brand new one got here out round each 5 years, with the final one showing in 2008. He died in 2010.

Who was Peter Kennedy? He was a Canadian econometrician born in 1943 and lived till 2010 who spent his complete profession kind of I feel at Simon Fraser. He did his PhD at Wisconsin in 1968 underneath Richard Daly — Wisconsin being an influence home in econometrics for a few years, to at the present time, and principally with out interruption. To be an econometrician educated there within the 60s by means of the 80s specifically, although, was to be educated by a number of the greatest.

Kennedy was thought-about an exceptional instructor of econometrics. He gained the 3M Nationwide Educating fellowship in 1987. He helped develop Simon Fraser’s Studying and Educational Improvement Middle and the ebook got here out, as an extension, of that intuition in that it was a ebook about what econometricians have been doing once they write down proofs. It was geared toward closing this hole between the technical textual content and the practitioner’s instinct. And he used simplicity and a objective to assist folks in a wide range of methods to simplify unnecessarily complicated issues, like his use of the ten commandments of econometrics which was a really useful pedagogical machine.

What’s new and what’s previous

A person purchased Abraham Lincoln’s authentic axe at a flea market. However in the future, the wood deal with broke. So he changed it with a brand new one, practically an identical in look. However then a 12 months later, the axe head broke. So he had a blacksmith make a reproduction and changed it. So. Is it nonetheless Abraham Lincoln’s axe?

The mixtape’s modifications have been sufficient within the second version that it bought a brand new identify although it seems to be the second version. Yale needed to do it that method — one thing concerning the metadata. I didn’t complain. It wasn’t precisely a changed axe head and wood deal with, nut it could be a brand new axe head and a barely modified deal with. And who is aware of — perhaps within the third version, it’ll be a modified deal with too.

First what’s the identical? The DAG stuff is generally the identical although I shaved off the pattern choice stuff. I don’t have practically the DAG-centric perspective as I did earlier than, although for pedagogical causes, I nonetheless assume they’re useful for explaining confounders and instrumental variables in addition to causality itself. Plus it’s an essential space and the hope is that may proceed to be an avenue into that literature if somebody desires to pursue it.

The potential outcomes chapter can also be very a lot the identical, perhaps 90-95%. Important modifications are new empirical examples. I added one thing from trade, in addition to considered one of my favourite papers — a paper by Jensen and Miller on Giffen habits. Which I take into account to be an actual vindication of neoclassical microeconomics as a theoretical framework because the Giffen good is a very uncommon phenomena, making precise theoretical predictions, and lots of distinguished economists together with I’m instructed George Stigler have been embarrassed by its inclusion in our books. And but it was plain and got here from fundamental first rules of utility maximization. It didn’t require stronger assumptions even in contrast to the third regulation of Hicksian demand, as an illustration, which requires a composite value index and three items for its proof. Giffen is there and will even be Marshallians first regulation of demand as a corollary. And I needed folks to see that testable predictions are rescued by causal inference and the randomized trial specifically.

However after that, every subject tends to open up a bit extra. Instrumental variables was up to date although not by a lot. Regression discontinuity bought optimum bandwidths and a brand new empirical instance. I dropped the shut election because the empirical instance and went with one thing that was extra canonical.

However the greatest modifications have been then to unconfoundedness and panel information. First, I dropped the chance and regression chapter. In the future I’ll write a mixtape type ebook nearly that, based mostly on my Harvard phd course from the spring of the identical identify. However not within the new ebook. I dropped it.

However the issue was that in dropping it, I had to determine the place to place regression. Plus Frisch-Waugh-Lovell is how Bacon proves the Bacon decomposition theorem for staggered adoption diff-in-diff and two method fastened results. So I made a decision to place it into the brand new unconfoundedness chapter, however by placing it there, your complete chapter grew to become imbalanced by this evident query — why use propensity scores or matching or stratification in the event you can simply run a regression. And answering that took a very long time for me, as I needed to discover a strategy to then restructure your complete chapter which actually helped me emphasize then all through heterogenous therapy results, widespread help and extrapolation. Fortunately that serviced the entire ebook’s thesis, however my level is it additionally made it evident to me if nobody else the place the ebook didn’t toe the road constantly on that time too.

After which in fact diff-in-diff and artificial management. Your entire second a part of the ebook is on panel information, and I might’ve simply as simply damaged the ebook into two volumes if I needed, with one on panel information, however I didn’t. I’m curious how the backbone of the ebook will maintain up with it now being 800 pages. However diff-in-diff is essential, and its developments during the last ten years deserves shut consideration. Even then, it felt like I used to be by no means going to be finished, so it stays what seems like a selective but essential protection of that new literature.

After which there’s the brand new synth chapters. I cowl how I learn the developments since Abadie and Gardeazebal’s mannequin first appeared within the AER in 2003. That’s the place I cowl augmented synth, which is a callback to the bias adjustment methodology that Abadie and Imbens developed for matching that I cowl within the unfoundedness, and it’s the place I additionally introduce frivolously penalized regression, with ridge. I additionally cowl matrix completion and artificial diff-in-diff.

We navigate our historic lives with tales

However in all probability the bizarre change is the narrative backbone of the ebook, and that’s my choice to make what I name “the biography of causal inference” a central organizing precept of the ebook. And that’s this: that causal inference in economics as we all know it has been closely influenced by two separates streams. Orley Ashenfelter, the Princeton Industrial Relations Part, program analysis, and the prioritization of “credibility” in response to an empirical disaster in quantitative labor economics within the Seventies and Eighties. And that credibility quest being explicitly a shift from mannequin to design, and quasi-experimental design specifically.

The second stream is the Harvard statistics division on the similar period as Orley led by the evangelism and scientific improvements of Don Rubin, and his extensions to the potential outcomes framework, and the connection between the experimental design and non-experimental ones too.

I’m not considered one of these ones who sees Roy because the supply of the potential outcomes modeling. I see it in Hume by means of Mill, David Lewis, Neyman and Fisher. However I feel the downgrading of Rubin’s position and the elevation of Roy is, in my private opinion, revisionist historical past. It’s very clear to me that potential outcomes wouldn’t be as it’s at present with out Rubin, which is why I have a tendency to emphasise the biography and sociology of causal inference over merely the concepts’ origins.

After which in fact — Josh Angrist, a scholar of Orleys from Princeton, dyed within the wool devotee to quantitative labor as made manifest within the Part, with a deep appreciation of what randomization buys for us, and instrumental variables specifically, and Guido Imbens, the younger econometrician from Brown who will get a name from Gary Chamberlain in the future, after the ASSA is over for a job he by no means even interviewed for, and for which Angrist himself voted towards hiring him of their division assembly no much less! That one 12 months overlap between these two younger males would result in the LATE, a decade of labor re-imagining and reconstructing instrumental variables across the potential outcomes modeling, and actually operate as a gate for Rubin’s frameworks to enter utilized work. It’s true that Heckman and Robb launched economists in all probability to potential outcomes in 1985, which until you depend Roy (which has no outright notation even when the thought of important heterogeneity and sorting on therapy positive aspects is there) was the primary time we see PO in economics, I feel it was Imbens econometric zeal and analysis agenda over a long time that carried kicking and screaming, and Josh’s relentless boldness and creativity in utilized work too.

In order that triangle — Orley, Rubin bridged by Angrist and Imbens — is the skeleton of the ebook.

However why? Why did I do this? And the reply is definitely easy. The primary is that I feel we want private tales to navigate our personal historic lives. We have to perceive the place it got here from. Peter a Kennedy gave us the Ten Commandments of econometrics, however I feel it’s simply as essential to listen to how Israel bought to be within the place and place they have been the place the availability and demand of these two tablets got here to exist in any respect. I needed readers to see that the form of causal inference is what it’s due to folks, locations and fights earlier than us all.

Which results in the second factor. Why does causal inference so usually really feel like a international, alien virus even to folks with precise coaching in quantitative strategies? Why does it really feel like two individuals are utilizing comparable language utilizing comparable instruments however in some way nonetheless speaking previous each other?

That form of factor is much less a group of instruments as it’s a worldview or a paradigm. And paradigms are inclined to not exist alongside each other peacefully. They are typically monopolistic and imperialistic as a result of they are saying two issues without delay. They are saying you might be fallacious. And so they say I’m proper. And such rights can elevate the emotions all of us had in highschool relying on the place we have been within the pecking order and hierarchy of our personal lives — on the high in the event you’re a winner, or on the backside in the event you’re an outsider.

And a part of the objective of utilizing these tales is just to assist discover those who don’t come from Princeton-Cambridge’s labor custom. Whose professors in class weren’t the descendants of Orley Ashenfelter, even when they themselves have been labor themselves. As I would like folks to seek out the highway maps that permit them perceive this worldview referred to as typically the “credibility revolution” and I needed folks to perhaps really feel as if they really belong. That all of us belong. Not simply on this occupation, however to life and existence itself — the broader group, not simply the cliques in our jobs.

And I stay satisfied that particular tales are when instructed properly in a position to do this. Which once more leads again to the primary objective of my life and these books — I wish to be myself, write how I wish to write, use no matter means obligatory, to assist construct as many bridges to whoever and wherever so that individuals can write the papers which are of their hearts.

In order that’s all, that’s the newest. Countdown is beginning. I’m excited.

[ad_2]

Agentic AI vs Automation: Key Variations Defined

[ad_1]

This scene is enjoying out throughout engineering groups in all places.

Somebody wraps just a few LangChain calls inside a loop, provides a few instruments, and proudly declares, “We’ve constructed an AI agent.” The demo seems nice. Everyone seems to be impressed.

Then it goes to manufacturing.

The primary sudden enter arrives. The workflow breaks. Logs refill. Alerts begin firing. Instantly, you’re debugging the system in the midst of the night time.

The issue isn’t the code. It’s that automation and agentic AI are essentially totally different.

Treating an automation like an AI agent, or anticipating an agent to behave like a deterministic workflow, results in unpredictable failures. Your “agent” may ship the identical e-mail to a buyer 47 occasions, skip essential steps, or make selections you by no means meant.

Understanding the place automation ends and the place agentic AI begins isn’t only a technical distinction. It’s the distinction between constructing dependable programs and creating costly, hard-to-debug issues.

Agentic AI vs Automation

AutomationAgentic AI
Execute predefined workflowsObtain a objective, whatever the actual path
Follows fastened guidelines and logicMakes selections primarily based on context and observations
Predetermined sequence of stepsDynamic sequence determined throughout execution
Can not adapt past programmed guidelinesAdjustments technique when situations change or failures happen
Developer controls each stepDeveloper defines the target; the agent decides the steps
Works finest with structured, anticipated inputsCan deal with ambiguous and unstructured inputs
Stateless except explicitly programmedMaintains reminiscence of earlier actions and outcomes
No planning functionalityPlans, reprioritizes, and selects the subsequent motion
Stops or throws an error when assumptions breakMakes an attempt different approaches earlier than failing
Instruments are known as in a set orderChooses which device to make use of primarily based on the present state
Extremely predictable and deterministicMuch less predictable however extra versatile
Straightforward to hint each stepRequires logging of reasoning and resolution historical past
Greatest fitted to ETL pipelines, bill processing, compliance checks, and scheduled storiesGreatest fitted to analysis brokers, coding assistants, buyer assist, and multi-step downside fixing
Instance: A each day gross sales report generated utilizing fastened enterprise guidelinesInstance: A analysis agent deciding whether or not to look, collect extra data, or summarize
Can not function outdoors predefined guidelines (e.g., a modified CSV schema breaks the workflow)Could make sudden selections if guardrails and bounds will not be outlined

What is AI Automation?

Consider automation as a merchandising machine. You choose B4, and the machine responds the identical means each single time.

Automation offers you direct management: you define how issues needs to be performed and in what order. Whether or not it’s a cron job from 2008 or a contemporary knowledge pipeline, automation does precisely what you advised it to do.

And truthfully, automation is underrated. It’s quick, auditable, and predictable. Bill processing, ETL pipelines, compliance checks, nightly stories: these are automation issues, solved fantastically by automation. Including “agent” to the outline doesn’t make them higher. 

Fingers-on: A Easy Automation Pipeline

def run_daily_report(input_path: str, output_path: str):
    df = pd.read_csv(input_path)
    df["processed_at"] = datetime.now().isoformat()
    df["high_value"] = df["revenue"] > 10000  # fastened rule, all the time
    df.to_csv(output_path, index=False)
    print(f"Finished. {len(df)} rows processed.")

run_daily_report("gross sales.csv", "daily_report.csv") 

Output:

Output

Now rename the “income” column to “whole” within the supply CSV. The pipeline breaks. That’s the limitation of automation: it really works completely inside its body, and fails the second it steps outdoors it.

Output

What’s Agentic AI? 

An agent behaves like a contractor. You say “construct me a deck by Friday,” and that’s the entire transient. They deal with the permits, the supplies, the climate delays, and the construct sequence, none of which you specified. They understand the scenario, type a plan, act, observe the outcomes, and regulate.

The primary options of an actual agent are: 

  • A objective as an alternative of a listing, it is aware of what constitutes the tip of the method, not simply the subsequent steps; 
  • Sensible planning, it may resolve on the suitable instruments primarily based on the earlier experiences; 
  • The reminiscence, it can observe what has been performed earlier than, and the way; 
  • The adaptability, if it fails, it manages to modify the techniques as an alternative of falling aside. 

Fingers-on: Construct a Minimal Agent Loop 

This can be a analysis agent that has the identical intention each time, but it surely chooses the route itself, relying on its earlier data.

class ResearchAgent:
    def __init__(self, instruments: dict):
        self.instruments = instruments
        self.reminiscence = {"findings": [], "objective": None}

    def decide_next_action(self) -> str:
        if not self.reminiscence["findings"]:
            return "search_web"          # nothing but, begin looking
        if len(self.reminiscence["findings"]) < 3:
            return "fetch_detail"        # want extra depth
        return "write_summary"           # sufficient to summarize

    def run(self, objective: str) -> str:
        self.reminiscence["goal"] = objective
        for _ in vary(10):              # all the time cap your loops
            motion = self.decide_next_action()
            end result = self.instruments[action](self.reminiscence)
            self.reminiscence["findings"].append(end result)
            if motion == "write_summary":
                break
        return self.reminiscence["findings"][-1]

Output:

Output

The strategy decide_next_action() is all it takes. The agent finds out what it is aware of with a purpose to act. In case you need to enhance your code, introduce a brand new situation wherein the agent makes use of search_alternative if search_web offers empty outcomes. That is known as adaptation, and machines can’t do it. 

The fundamental course of: detect → assume → act → change → return to the start. 

The place Most Methods Really Fall

An inconvenient fact: most programs known as “brokers” as we speak are automation with an LLM bolted onto one step. The LLM fills in a type or classifies some enter, and the subsequent step runs no matter what it determined. That’s not company. It’s a fancier merchandising machine.

A extra sincere classification: 

DegreeHabitsActual Instance
Fundamental automationFastened steps, no LLMCron job, ETL pipeline
LLM-assisted automationFastened steps, LLM at one nodeRAG with hardcoded retrieval
Partially agenticLLM chooses instruments, objective is fastenedReAct agent with a device registry
Totally agenticLLM units sub-goals, builds instrumentsSelf-directed analysis or coding brokers

Most business deployments sit at stage 2 or 3, and that’s wonderful. Degree 3 is a genuinely good use of the expertise. The issue begins when a staff claims stage 4 whereas delivery stage 2, then can’t determine why it falls aside outdoors the comfortable path.

Facet-by-Facet: Buyer Assist Ticket Handler

Similar downside, two programs: categorize the ticket, write a response.

The Automation Model

def handle_ticket(ticket_text: str) -> dict:
    class = classify(ticket_text)       # all the time runs
    template = get_template(class)      # all the time runs
    response = fill_template(template, ticket_text)  # all the time runs
    return {"class": class, "response": response}

Output:

Output

Quick, predictable, low-cost to run. However it may’t verify order historical past, flag a VIP buyer, or ask a clarifying query. Each ticket will get the identical therapy: “URGENT, you charged me twice and my account is locked” will get dealt with precisely like “The place is my order?

The Agentic Model 

def handle_ticket_agentic(ticket_text: str, instruments: dict) -> dict:
    state = {"ticket": ticket_text, "historical past": [], "resolved": False}
    for _ in vary(8):                     # bounded loop
        next_action = llm_decides(state)   # LLM picks the subsequent device
        end result = instruments[next_action](state)
        state["history"].append({"motion": next_action, "end result": end result})
        if next_action == "resolve":
            state["resolved"] = True
            break
    return state

Output:

Output

Right here, the trail is set at runtime. For the pressing billing message, the agent may verify account standing and transaction historical past, flag the billing difficulty, and escalate earlier than responding. For “The place is my order?”, it resolves in a few steps utilizing the delivery API. Similar system, totally different route, primarily based on what the ticket truly wants.

The way to Select Between Them? 

This isn’t about which expertise is newer. It’s in regards to the form of the issue.

Use automation when:

  • The duty follows the identical, auditable process each time
  • Pace issues greater than flexibility
  • Compliance requires each step to be traceable
  • You’re working the identical operation at excessive quantity

Use Agentic AI when:

  • The appropriate sequence of steps is determined by what’s found alongside the best way
  • The enter is unstructured (emails, paperwork, conversations)
  • A failure wants a brand new method, not only a retry from the highest
  • The issue is genuinely open-ended

Conclusion 

Automation is constructed to be predictable. Agentic AI is constructed to be adaptable. Neither is healthier; they remedy totally different issues.

“Agent” sounds extra spectacular than “pipeline,” so groups attain for it even when what they’ve constructed is nearer to the latter. When that pipeline breaks on some edge case and somebody asks why the agent failed, the sincere reply is normally that it was by no means actually an agent.

The higher place to begin is automation. Map out the place it really works and the place it hits a wall. Attain for agentic habits solely the place automation genuinely can’t go.

Incessantly Requested Questions

Q1. What’s the primary distinction between automation and agentic AI?

A. Automation follows predefined workflows, whereas agentic AI adapts its actions to attain a objective primarily based on altering context.

Q2. When do you have to use agentic AI as an alternative of automation?

A. Use agentic AI when duties require planning, adaptation, device choice, or dealing with ambiguous and unstructured inputs.

Q3. Why do many AI brokers fail in manufacturing?

A. Many are fastened automation workflows with an LLM added, missing true planning, reminiscence, and adaptive decision-making.

Information Science Trainee at Analytics Vidhya
I’m presently working as a Information Science Trainee at Analytics Vidhya, the place I concentrate on constructing data-driven options and making use of AI/ML strategies to resolve real-world enterprise issues. My work permits me to discover superior analytics, machine studying, and AI purposes that empower organizations to make smarter, evidence-based selections.
With a robust basis in pc science, software program improvement, and knowledge analytics, I’m keen about leveraging AI to create impactful, scalable options that bridge the hole between expertise and enterprise.
📩 You may as well attain out to me at [email protected]

Login to proceed studying and luxuriate in expert-curated content material.

[ad_2]