
[ad_1]
A number of official SAP npm packages had been compromised in what’s believed to be a TeamPCP supply-chain assault to steal credentials and authentication tokens from builders’ techniques.
Safety researchers report that the compromise impacted 4 packages, with the variations now deprecated on NPM:
- @cap-js/sqlite – v2.2.2
- @cap-js/postgres – v2.2.2
- @cap-js/db-service – v2.10.1
- mbt – v1.2.48
These packages help SAP’s Cloud Software Programming Mannequin (CAP) and Cloud MTA, that are generally utilized in enterprise improvement.
In accordance with new studies by Aikido and Socket, the compromised packages had been modified to incorporate a malicious ‘preinstall’ script that executes mechanically when the npm bundle is put in.
This script launches a loader named setup.mjs that downloads the Bun JavaScript runtime from GitHub and makes use of it to execute a closely obfuscated execution.js payload.
The payload is an information-stealer used to steal all kinds of credentials from each developer machines and CI/CD environments, together with:
- npm and GitHub authentication tokens
- SSH keys and developer credentials
- Cloud credentials for AWS, Azure, and Google Cloud
- Kubernetes configuration and secrets and techniques
- CI/CD pipeline secrets and techniques and setting variables
The malware additionally makes an attempt to extract secrets and techniques straight from the CI runner’s reminiscence, just like how TeamPCP extracted credentials in earlier supply-chain assaults.
“On CI runners, the payload executes an embedded Python script that reads /proc/
“This reminiscence scanner for secrets and techniques is structurally similar to the one documented within the Bitwarden and Checkmarx incidents.”
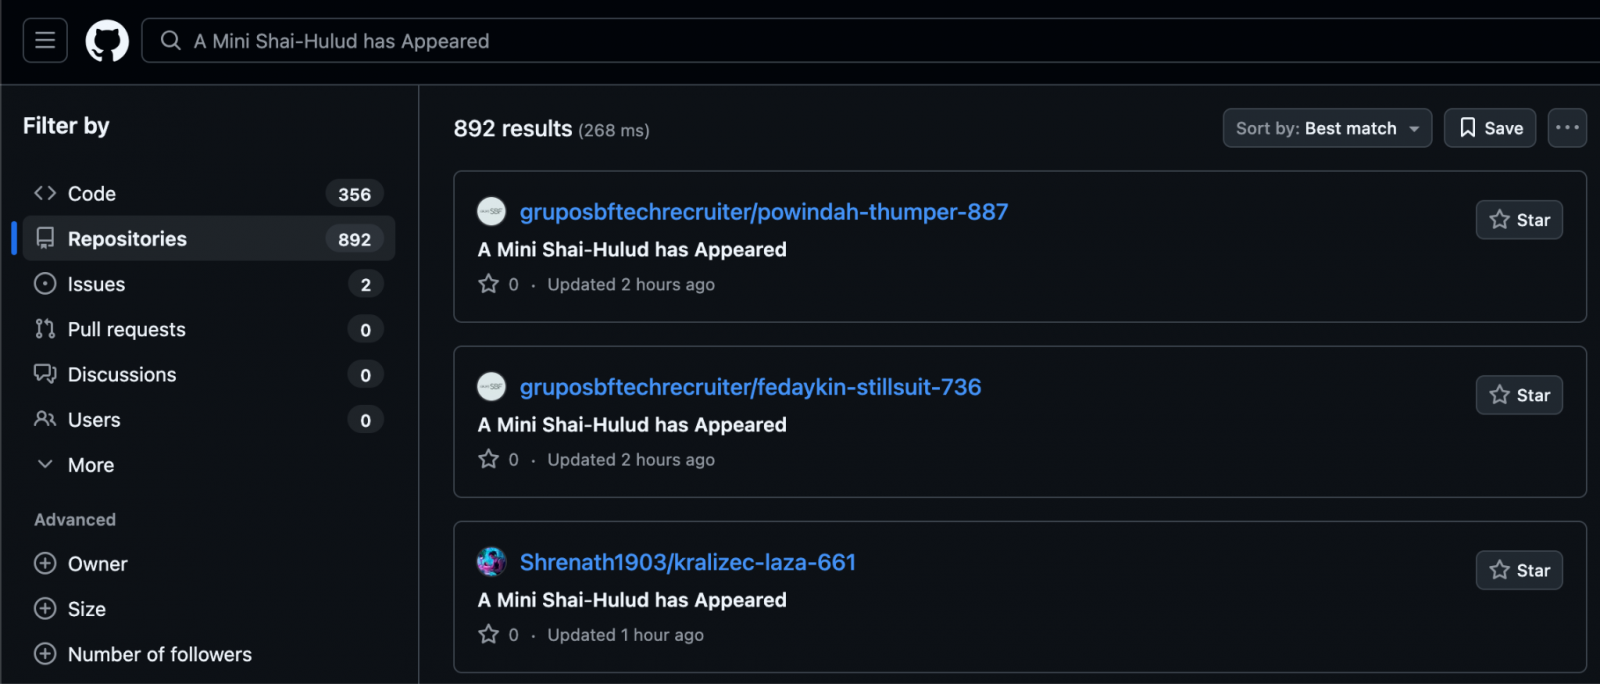
As soon as knowledge is collected, it’s encrypted and uploaded to public GitHub repositories beneath the sufferer’s account. These repositories embody the outline, “A Mini Shai-Hulud has Appeared”, which can be just like the “Shai-Hulud: The Third Coming” string seen within the Bitwarden provide chain assault.
Supply: Aikido
The malware additionally depends on GitHub commit searches as a dead-drop mechanism to retrieve tokens and achieve additional entry.
“The malware searches GitHub commits for this string and makes use of matching commit messages as a token dead-drop,” explains Aikido.
“Commit messages matching OhNoWhatsGoingOnWithGitHub:
Much like earlier assaults, the deployed payload additionally contains code to self-propagate to different packages.
Utilizing stolen npm or GitHub credentials, it makes an attempt to switch different packages and repositories it positive aspects entry to, and injects the identical malicious code to unfold additional.
Researchers have linked this assault with medium confidence to the TeamPCP risk actors, who used comparable code and ways in earlier supply-chain assaults towards Trivy, Checkmarx, and Bitwarden.
Whereas it’s unclear how the risk actors compromised SAP’s npm publishing course of, Safety Engineer Adnan Khan studies that an NPM token might have been uncovered through a misconfigured CircleCI job.
BleepingComputer contacted SAP to find out how the npm packages had been compromised, however didn’t obtain a reply on the time of publication.
AI chained 4 zero-days into one exploit that bypassed each renderer and OS sandboxes. A wave of latest exploits is coming.
On the Autonomous Validation Summit (Might 12 & 14), see how autonomous, context-rich validation finds what’s exploitable, proves controls maintain, and closes the remediation loop.
[ad_2]

